Search results for tag #rust
StyleSmuggler: Magento and Adobe Commerce 0-day RCE under active attack
An unpatched zero-day vulnerability dubbed StyleSmuggler affects all current versions of Magento and Adobe Commerce, including 2.4.9, enabling unauthenticated remote code execution. Active exploitation began on September 4th, 2026. The attack operates in two stages: injecting malicious PHP code into Magento's template system using styles properties to evade safeguards, then executing the poisoned code via failed payment emails. Upon successful compromise, attackers deploy a Rust-based backdoor disguised as legitimate system processes (kworker, fc-cache, or chronyd) that connects to command and control servers. The backdoor uses NTP-shaped UDP traffic for C2 communication to evade detection. A second unrelated attacker has also been observed exploiting the same vulnerability to deploy PHP web shells. Affected merchants should deploy immediate mitigation measures, scan for compromise, and temporarily disable GraphQL until an official patch is released.
Pulse ID: 6a9ef14fbc62257cff38357b
Pulse Link: https://otx.alienvault.com/pulse/6a9ef14fbc62257cff38357b
Pulse Author: AlienVault
Created: 2026-09-07 17:15:59
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#0Day #Adobe #BackDoor #CyberSecurity #Email #InfoSec #Magento #OTX #OpenThreatExchange #PHP #RAT #RCE #RemoteCodeExecution #Rust #UDP #Vulnerability #ZeroDay #bot #AlienVault
Bypassing the Gatekeepers: How a Global Phishing Campaign Turns Google's Infrastructure into a Trust Proxy
Cybercriminals are exploiting legitimate Google infrastructure in a sophisticated phishing operation that bypasses email security gateways and enterprise firewalls. The attack chains together six distinct Google properties including Meet, Search, DoubleClick, Custom Search, Tag Manager and Analytics to proxy malicious traffic through trusted domains. Victims' email addresses are encoded in URL fragments and stripped before server-side logging. Landing pages dynamically impersonate target organizations by pulling live logos from Clearbit, capturing real-time website screenshots, and validating domains via Google's DNS API. The operation includes multilingual support for 16 languages and dual execution tracks: credential harvesting with immediate Telegram exfiltration, or silent ScreenConnect remote access tool installation. Lures span document reviews, credential expiry notices, package delivery, payment notifications, government benefits and voicemail themes targeting manufacturing, government, finance and...
Pulse ID: 6a9ef40735b49c55dc7166c9
Pulse Link: https://otx.alienvault.com/pulse/6a9ef40735b49c55dc7166c9
Pulse Author: AlienVault
Created: 2026-09-07 17:27:35
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#CredentialHarvesting #CyberSecurity #DNS #DoubleClick #Email #Google #Government #ICS #InfoSec #Manufacturing #OTX #OpenThreatExchange #Phishing #Proxy #RAT #Rust #ScreenConnect #Telegram #bot #AlienVault
Rust debugging survey 2026 results https://lobste.rs/s/ku4hwg #rust
https://blog.rust-lang.org/2026/09/07/rust-debugging-survey-2026-results/
Hackers Abuse Trusted Google Services to Hide Credential-Stealing Phishing Attacks
Indicators extracted from public reporting. Source: https://blog.knowbe4.com/bypassing-the-gatekeepers-how-a-global-phishing-campaign-turns-googles-infrastructure-into-a-trust-proxy
Pulse ID: 6a9ed07f2397dd4f16c59035
Pulse Link: https://otx.alienvault.com/pulse/6a9ed07f2397dd4f16c59035
Pulse Author: CyberHunter_NL
Created: 2026-09-07 14:55:59
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#CyberSecurity #Google #HTTP #HTTPS #InfoSec #OTX #OpenThreatExchange #Phishing #Proxy #RCE #Rust #bot #CyberHunter_NL
New BYOTC Attack Hijacks Trusted Windows Apps to Abuse Privileged Kernel Drivers
Indicators extracted from public reporting. Source: https://xusheng.dev/posts/byotc/main/
Pulse ID: 6a9ec2682f66491294927660
Pulse Link: https://otx.alienvault.com/pulse/6a9ec2682f66491294927660
Pulse Author: CyberHunter_NL
Created: 2026-09-07 13:55:52
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#CyberSecurity #HTTP #HTTPS #InfoSec #OTX #OpenThreatExchange #RCE #Rust #Windows #bot #CyberHunter_NL
Observation: If you are learning a new language (for me #Rust atm), you don't quite know yet what existing go-to libraries are and you start searching around.
Maybe that has always been the case in some form, but the amount of vibe-coded, only 1-2 releases in total, still with clear bugs and issues and then abandoned is just CRAZY.
Sure, I'm still learning and certainly not quick understanding why something doesn't work, but I've literally wasted many hours already b/c of slop-crates 🤬
It took a year to ship WebAssembly in Anubis by @cadey https://lobste.rs/s/aokzbg #rust #wasm
https://anubis.techaro.lol/blog/2026/anubis-wasm/

ClickFix Campaign Leverages Blockchain to Host Malicious Payloads
A large scale ClickFix threat campaign has compromised more than 5,400
legitimate websites. Attackers abuse trusted websites to display fake
CAPTCHA-style pages that trick users into manually executing malicious
commands while using blockchain based infrastructure to maintain
resilient payload delivery.
Pulse ID: 6a9d212bba61045a3e945aeb
Pulse Link: https://otx.alienvault.com/pulse/6a9d212bba61045a3e945aeb
Pulse Author: cryptocti
Created: 2026-09-06 08:15:37
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#BlockChain #CAPTCHA #CyberSecurity #InfoSec #OTX #OpenThreatExchange #Rust #bot #cryptocti
ClickFix Campaign Leverages Blockchain to Host Malicious Payloads
A large scale ClickFix threat campaign has compromised more than 5,400
legitimate websites. Attackers abuse trusted websites to display fake
CAPTCHA-style pages that trick users into manually executing malicious
commands while using blockchain based infrastructure to maintain
resilient payload delivery.
Pulse ID: 6a9d212beff3456cc91b1eec
Pulse Link: https://otx.alienvault.com/pulse/6a9d212beff3456cc91b1eec
Pulse Author: cryptocti
Created: 2026-09-06 08:15:38
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#BlockChain #CAPTCHA #CyberSecurity #InfoSec #OTX #OpenThreatExchange #Rust #bot #cryptocti
Credera is hiring Architect, Software Engineering
🔧 #java #javascript #python #ruby #rust #scala #dotnet #angular #react #springboot #cypress #aws #azure #cicd #docker #gcp #kubernetes #terraform #solutionsarchitect
🌎 Chicago, Illinois
⏰ Full-time
🏢 Credera
Job details https://jobsfordevelopers.com/jobs/architect-software-engineering-at-credera-com-jan-25-2026-0d443f?utm_source=mastodon.world&utm_medium=social&utm_campaign=posting
#jobalert #jobsearch #hiring
LaunchDarkly is hiring Senior Backend Engineer, Experimentation
🔧 #cplusplus #golang #python #rust #postgresql #seniorengineer
🌎 Remote; United States
⏰ Full-time
🏢 LaunchDarkly
Job details https://jobsfordevelopers.com/jobs/senior-backend-engineer-experimentation-at-launchdarkly-com-aug-21-2026-c134ee?utm_source=mastodon.world&utm_medium=social&utm_campaign=posting
#jobalert #jobsearch #hiring
Rust SIMD on the GPU https://lobste.rs/s/omhoxh #performance #rust
https://vectorware.com/blog/simd-on-gpu/
Visualizing Rust's Vtables: How dyn Trait Works In Memory https://lobste.rs/s/6du6h3 #rust
https://sofiabelen.github.io/projects/visualizing-rusts-vtables-how-dyn-trait-works-in-memory/
Informal #FPIndia gathering next Sunday in #Bangalore. This is *very* limited space, and informal, so we don't have a predefined agenda.
Come hang out, eat, drink, and have some chill conversations with fellow #FunctionalProgramming enthusiasts!
https://luma.com/xpbc4v4q
Is your company currently hiring for a role that includes using Rust?
Reply with a link to the opening and any relevant context.
If you're not, we'd appreciate a repost for visibility
MISRust: Mapping MISRA-C++ Coding Guidelines to the Rust Programming Language https://lobste.rs/s/naoawd #rust
https://arxiv.org/abs/2605.23490
Plush's New Register-Based Interpreter Is Insanely Fast https://lobste.rs/s/4xy1l4 #compilers #rust
https://pointersgonewild.com/2026-09-02-plushs-new-register-based-interpreter/
Rust trifft auf Agentic AI: Online-Konferenz betterCode() Rust im November
Die Online-Konferenz zeigt am 26. November, wie agentische Softwareentwicklung mit Rust gelingt und warum sich die Programmiersprache gut dafür eignet.
#Developer #IT #Programmiersprachen #Rust #Softwareentwicklung #news
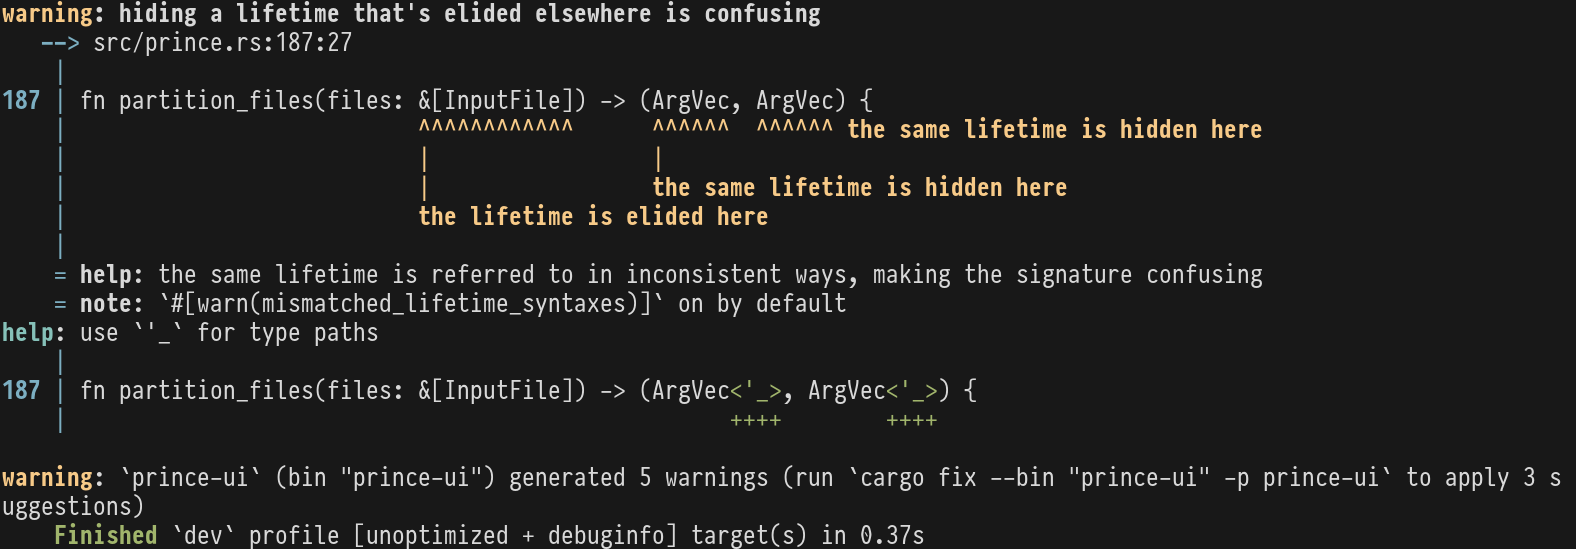
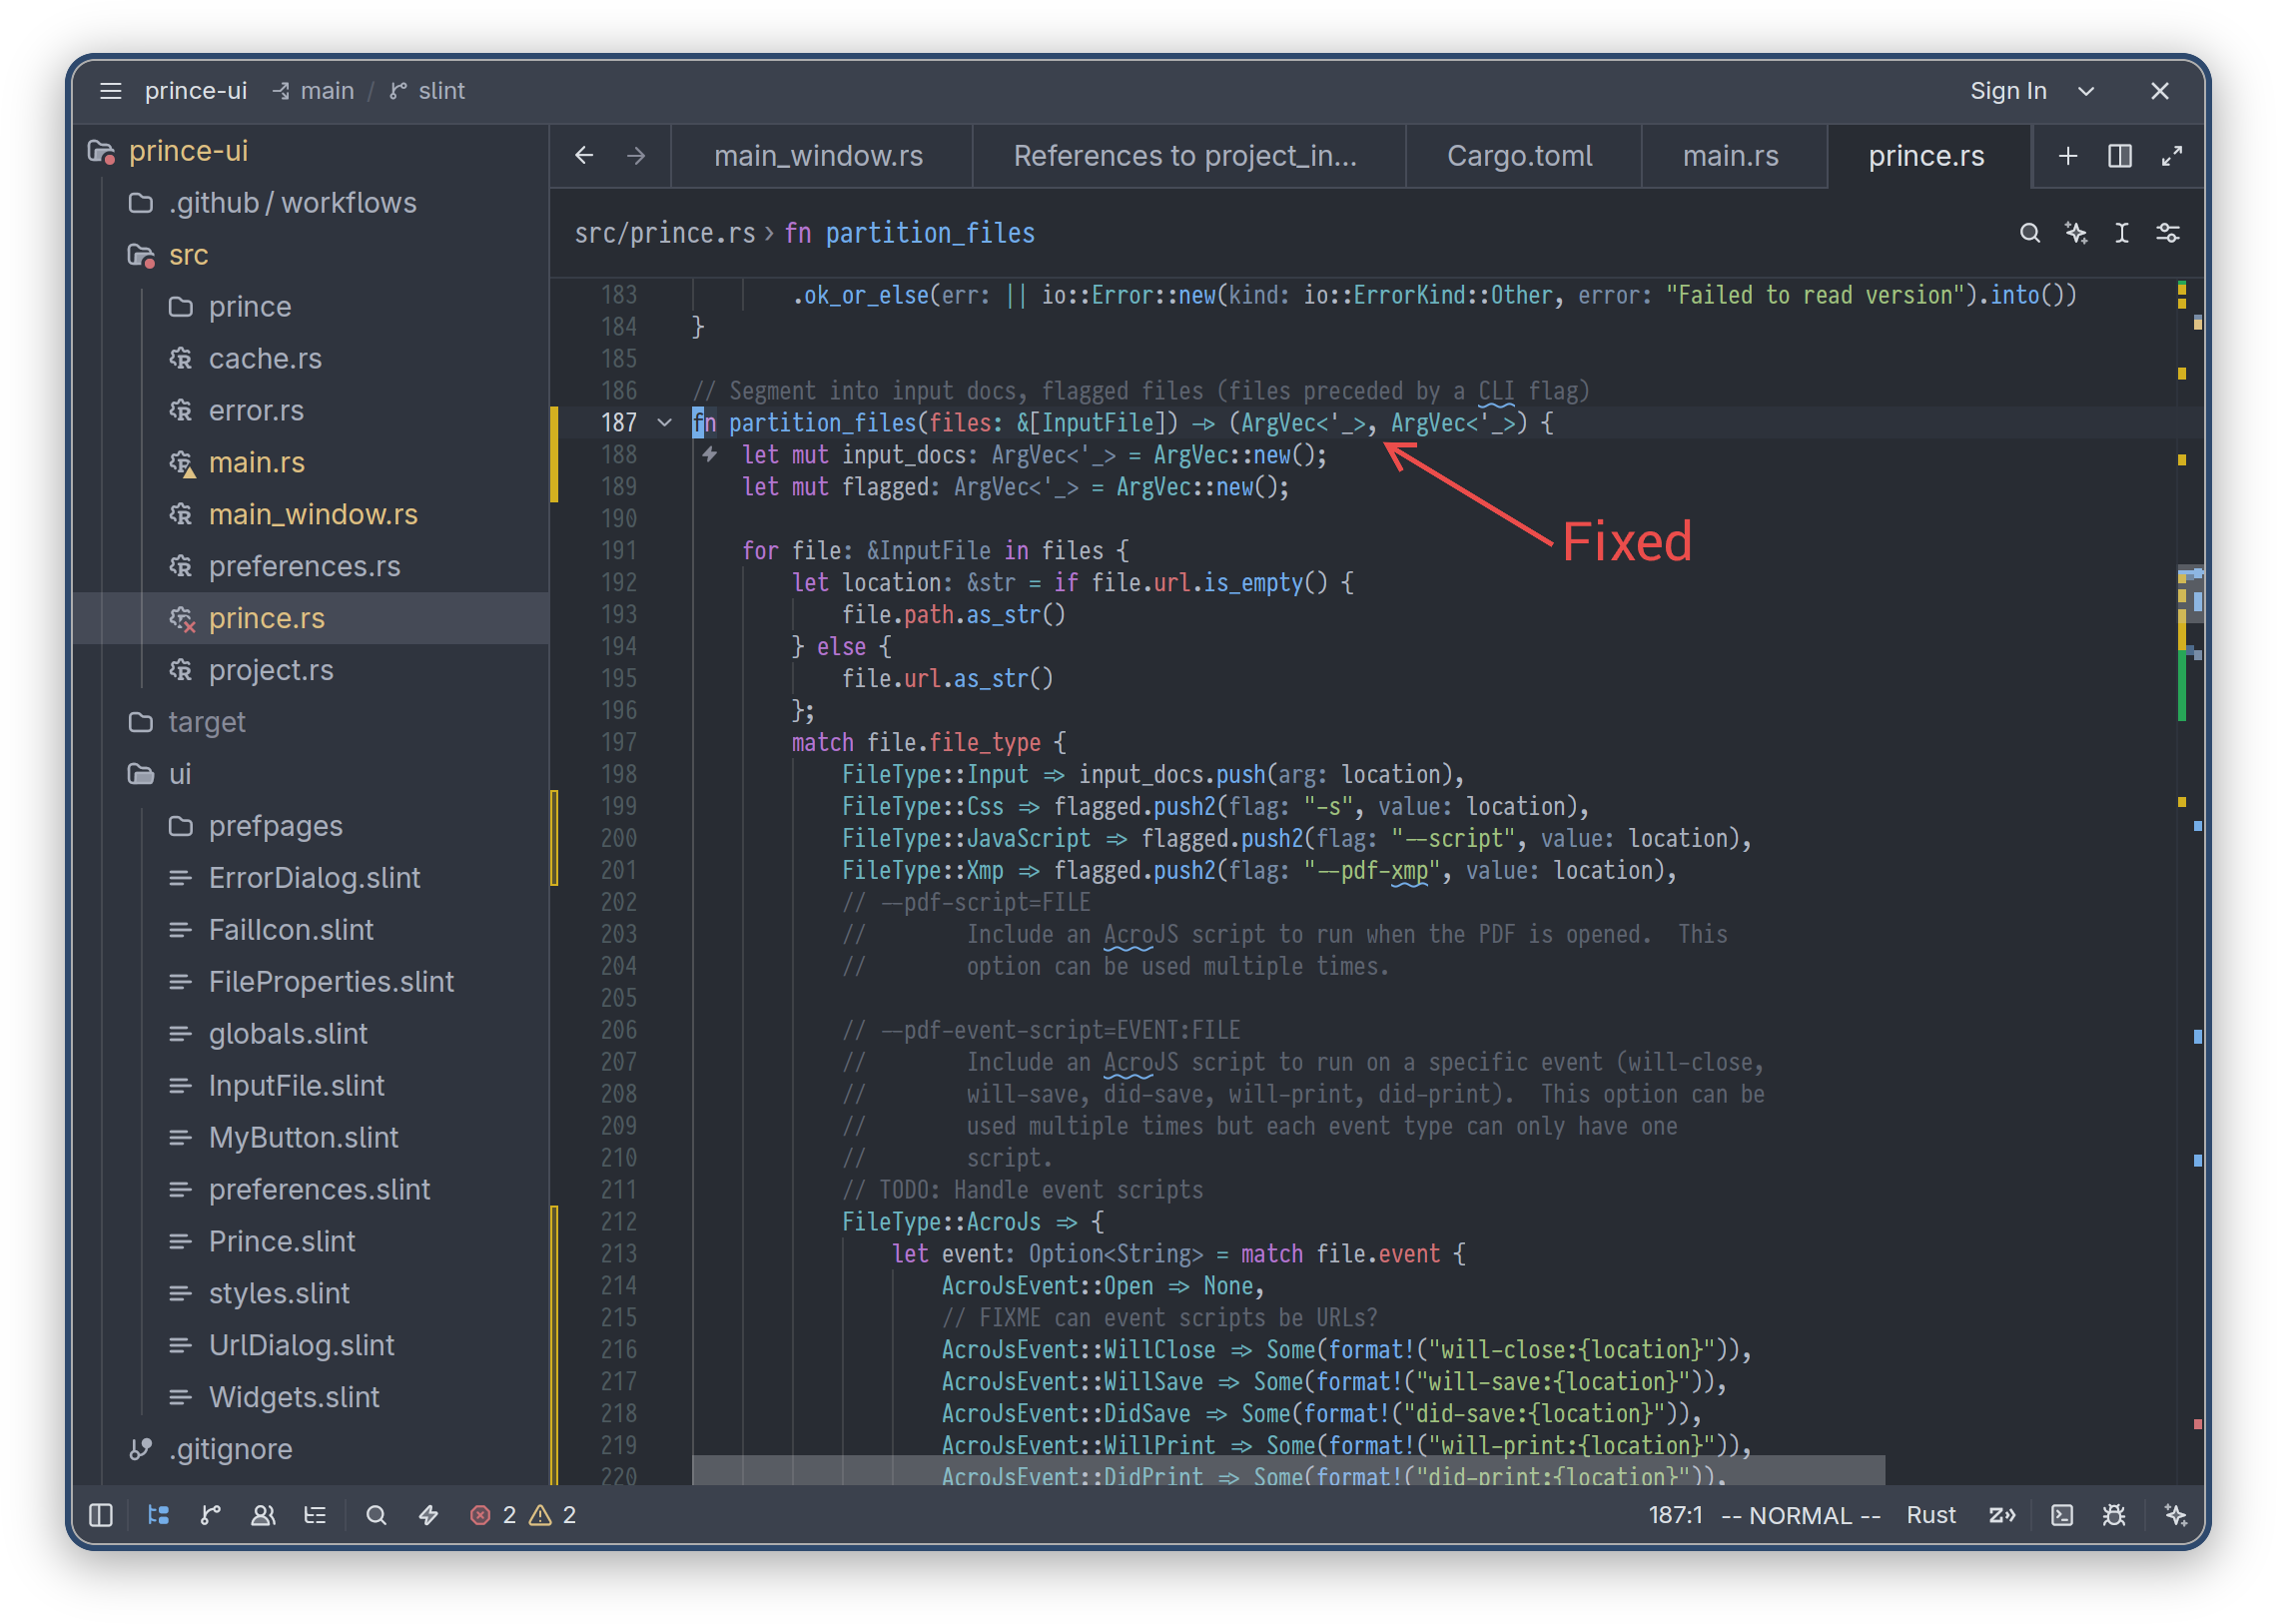
Ever see a #Rust compiler warning with a suggested fix and wish the compiler would do it for you? Well, good news! `cargo fix`—built into Cargo can do that.
The first screenshot shows a warning about elided lifetimes. The second screenshot shows the code after running `cargo fix`. It has applied the suggestion.
`cargo fix` is conservative, so you will usually need one of the `--allow` options to allow it make change. In my case I had all modified code staged in `git`, so used `--allow-staged`.
Alt...
warning: hiding a lifetime that's elided elsewhere is confusing
help: use `'_` for type paths:
fn partition_files(files: &[InputFile]) -> (ArgVec<'_>, ArgVec<'_>)
Alt...
The code has been updated to:
fn partition_files(files: &[InputFile]) -> (ArgVec<'_>, ArgVec<'_>) {
Introducing Compote, a successor to Figment via @aaronmallen https://lobste.rs/s/cnobln #release #rust
https://crates.io/crates/compote
Announcing Rust 1.98.1 https://lobste.rs/s/77qick #rust
https://blog.rust-lang.org/2026/09/03/Rust-1.98.1/
Malicious Apache Modules Turn Trusted Government Websites Into Stealth Phishing Proxies
Indicators extracted from public reporting. Source: https://research.checkpoint.com/2026/gaming-the-system-how-a-chinese-speaking-actor-turned-brazilian-government-sites-into-an-seo-weapon/
Pulse ID: 6a99281dd25ff4fe204d7a44
Pulse Link: https://otx.alienvault.com/pulse/6a99281dd25ff4fe204d7a44
Pulse Author: CyberHunter_NL
Created: 2026-09-03 07:56:13
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#APAC #Apache #Brazil #Chinese #CyberSecurity #Government #HTTP #HTTPS #InfoSec #OTX #OpenThreatExchange #Phishing #RCE #Rust #bot #CyberHunter_NL
Let's build a compressor from scratch https://lobste.rs/s/3y9lbw #compsci #programming #rust
https://ochagavia.nl/blog/lets-build-a-compressor-from-scratch/
One leftover build path links an infostealer, a remote-access tool, and a ransomware family
A compilation artifact, specifically a developer's home directory path (/home/tcherber/.cargo/), linked multiple malware families including a Rust-based infostealer named Zer0day Stealer, an HVNC remote-control tool, and ENIGMA Locker ransomware to a single developer. The infostealer exfiltrates cryptocurrency wallets, browser credentials, Office documents, and VPN configurations. The HVNC tool enables hidden remote desktop sessions and implements AMSI and ETW evasion techniques. Analysis revealed an actively developed, cross-platform malware operation spanning Windows, Linux, and macOS. Multiple droppers written in C, Rust, and PowerShell were discovered delivering the malicious payloads. Build timestamps indicated development occurred within weeks, and infrastructure leaked evidence of additional tools including FUD-Crypter, Botnet, and C2 Agent components, demonstrating how overlooked compilation artifacts enable comprehensive attribution and threat mapping.
Pulse ID: 6a9756cad8fd625876d6a1a5
Pulse Link: https://otx.alienvault.com/pulse/6a9756cad8fd625876d6a1a5
Pulse Author: AlienVault
Created: 2026-09-01 22:50:50
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#Browser #CyberSecurity #InfoSec #InfoStealer #Linux #Mac #MacOS #Malware #OTX #Office #OpenThreatExchange #PowerShell #RAT #RansomWare #Rust #VNC #VPN #Windows #bot #botnet #cryptocurrency #hVNC #AlienVault
Implementing FMA and finding bugs in C and Rust standard libraries https://lobste.rs/s/qq9jpo #c #rust
https://shnatsel.github.io/implementing-fma-finding-bugs-in-std/
Gaming the system: how a Chinese-speaking actor turned Brazilian government sites into an SEO weapon
A Chinese-speaking cybercrime group dubbed Gambling Goblin has conducted a sustained campaign against Brazilian organizations since mid-2025, primarily targeting government and educational institutions. The attackers compromise web servers and install malicious Apache modules that silently reverse-proxy visitors to phishing pages while appearing to originate from legitimate domains. These phishing pages impersonate trusted app stores like Google Play and Microsoft Store but actually promote online gambling and sports betting. The operation manipulates search engine rankings by chaining together compromised high-reputation domains, particularly Brazilian government sites. The group deploys an extensive Linux toolkit including custom downloaders, backdoors, credential stealers, and reconnaissance tools, most heavily obfuscated to evade detection. Evidence shows the operation extends beyond Brazil with parallel infrastructure targeting Vietnamese, Spanish, and English-speaking victims.
Pulse ID: 6a982735d832e36397a5fad9
Pulse Link: https://otx.alienvault.com/pulse/6a982735d832e36397a5fad9
Pulse Author: AlienVault
Created: 2026-09-02 13:40:05
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#APAC #Apache #BackDoor #Brazil #Chinese #CyberCrime #CyberSecurity #Education #Google #GooglePlay #Government #InfoSec #Linux #Microsoft #OTX #OpenThreatExchange #Phishing #Proxy #RAT #Rust #Vietnam #bot #AlienVault
Counterfeit installers to system compromise: Tracking a deceptive software download campaign
A malware campaign uses counterfeit software-download websites impersonating trusted vendors to distribute malicious installers. The activity primarily targets China-based operations of multinational organizations and Chinese-speaking users across healthcare, manufacturing, gaming, technology, logistics, government, and education sectors. Malicious installers deploy payloads that establish persistence, disable security protections, and communicate with attacker-controlled infrastructure. The campaign employs dynamically generated installers with rotating hashes, spoofed vendor pages on .com.cn and .hl.cn domains, and randomized payload staging paths. Follow-on activity includes disabling Windows Defender, deleting shadow copies, neutralizing Windows Update, creating scheduled tasks for persistence, and establishing command-and-control over non-standard ports. Microsoft assesses this activity aligns with publicly reported Silver Fox operations but has not attributed it to a nation-state actor.
Pulse ID: 6a97908e94bd394c915c1cb9
Pulse Link: https://otx.alienvault.com/pulse/6a97908e94bd394c915c1cb9
Pulse Author: AlienVault
Created: 2026-09-02 02:57:18
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#China #Chinese #CyberSecurity #Education #Government #Healthcare #ICS #InfoSec #Malware #Manufacturing #Microsoft #OTX #OpenThreatExchange #RAT #Rust #Troll #Windows #bot #AlienVault
RISC-V interpreter from the future https://lobste.rs/s/potdi9 #assembly #rust
https://abundance.build/blog/2026-08-31-risc-v-interpreter-from-the-future/
Package manager pnpm 12 speeds itself up with Rust
With the release of the pnpm package manager to version 12 in Rust, the first benchmarks are now showing gains of up to 90 percent.
Paketmanager pnpm 12 beschleunigt sich selbst mit Rust
Mit der Veröffentlichung des Paketmanagers pnpm auf Version 12 in Rust gibt es nun die ersten Benchmarks, die Gewinne von bis zu 90 Prozent zeigen.
Financially Motivated Threat Actor Targets Brazil
Beginning in 2024, a financially motivated threat actor designated BREEZE COMET has conducted sophisticated operations targeting Brazilian financial services, retail, and eCommerce organizations. The group specializes in manipulating payment systems including Pix, STR, and Boleto to conduct fraudulent transfers worth tens of thousands of USD. Their evolved tactics leverage customized malware suites written in multiple languages including Rust, Nim, Golang, and Java, alongside compromised government websites for initial access and command and control. The threat actor demonstrates advanced capabilities by targeting banking software, payment APIs, and mTLS credentials while maintaining persistent access through multiple backdoors. Evidence indicates BREEZE COMET uses generative AI to accelerate malware development and script creation, suggesting potential expansion to other Latin American and African countries based on infrastructure replication observed in Nigeria, Paraguay, Ghana, and Venezuela.
Pulse ID: 6a9679441f068d4ee93916ae
Pulse Link: https://otx.alienvault.com/pulse/6a9679441f068d4ee93916ae
Pulse Author: AlienVault
Created: 2026-09-01 07:05:40
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#Africa #BackDoor #Bank #Brazil #CyberSecurity #Golang #Government #ICS #InfoSec #Java #LatinAmerica #Malware #Nim #OTX #OpenThreatExchange #RAT #RCE #Rust #TLS #bot #AlienVault
Hackers Compromise Cisco Routers to Spy on Networks and Reach Critical Infrastructure
Indicators extracted from public reporting. Source: https://www.sygnia.co/blog/fire-ant-evolves-from-hypervisors-to-trusted-infrastructure/
Pulse ID: 6a96851e018bc0914281849e
Pulse Link: https://otx.alienvault.com/pulse/6a96851e018bc0914281849e
Pulse Author: CyberHunter_NL
Created: 2026-09-01 07:56:14
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#Cisco #CyberSecurity #HTTP #HTTPS #InfoSec #OTX #OpenThreatExchange #RCE #Rust #Sygnia #bot #CyberHunter_NL

Shrimply: open source video editor with GPU path tracing and Manim integration https://lobste.rs/s/riufop #video #graphics #rust
https://github.com/soirihiroka/shrimply
RangeFrom, Part 2..: What I think is wrong about the design https://lobste.rs/s/hyn2bt #rust
https://erk.dev/2026/08/30/rangefrom-part-2
An Inside Look at Voice Phishing Campaigns in Microsoft Teams
Between January and April 2026, a coordinated social engineering operation named Spring Ring leveraged external Microsoft Teams accounts to impersonate IT help desk personnel, targeting over 150 employees across at least 10 companies. Adversaries initiated voice phishing calls to coerce victims into executing remote monitoring and management tools or custom malware. In advanced variants, attackers transitioned from vishing to NTLM relay attacks targeting domain controllers. Two distinct campaigns were observed: Campaign A utilized RMM tools and obfuscated PowerShell-based RATs, while Campaign B employed tailored cloud infrastructure with PetitPotam exploitation for domain-level compromise. The operation demonstrates the weaponization of trusted collaboration platforms as primary attack vectors, exploiting the trust gap in SaaS applications.
Pulse ID: 6a95603cd2ee92923d1e1dff
Pulse Link: https://otx.alienvault.com/pulse/6a95603cd2ee92923d1e1dff
Pulse Author: AlienVault
Created: 2026-08-31 11:06:36
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#Cloud #CyberSecurity #DomainController #InfoSec #Malware #Microsoft #MicrosoftTeams #OTX #OpenThreatExchange #Phishing #PowerShell #RAT #RCE #Rust #SocialEngineering #Troll #bot #AlienVault
Could Cargo's scheduler be better? https://lobste.rs/s/by7xg6 #compilers #rust
https://spirali.github.io/blog/cargo-scheduler/
China-Linked Fire Ant Hijacks Cisco Routers to Steal Credentials and Blind Security Logs
Indicators extracted from public reporting. Source: https://www.sygnia.co/blog/fire-ant-evolves-from-hypervisors-to-trusted-infrastructure/
Pulse ID: 6a955db9db6b038b8c55afeb
Pulse Link: https://otx.alienvault.com/pulse/6a955db9db6b038b8c55afeb
Pulse Author: CyberHunter_NL
Created: 2026-08-31 10:55:53
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#China #Cisco #CyberSecurity #HTTP #HTTPS #InfoSec #OTX #OpenThreatExchange #RCE #Rust #Sygnia #bot #CyberHunter_NL