Search results for tag #rust

Rewriting Bun in Rust https://lobste.rs/s/6rkdik #rust #vibecoding #zig
https://bun.com/blog/bun-in-rust
 🍵

So the bad news is I have been laid off.
The good news is that I'll have a lot more time to write in the short term, both book stuff and code stuff.
...anyone need a #rust programmer?
RootAsRole 4.0: Mehr Kontrolle als bei sudo
RootAsRole 4.0 erweitert die sudo-Alternative um ein neues Ausführungsmodell und feinere Richtlinien für privilegierte Linux-Befehle.
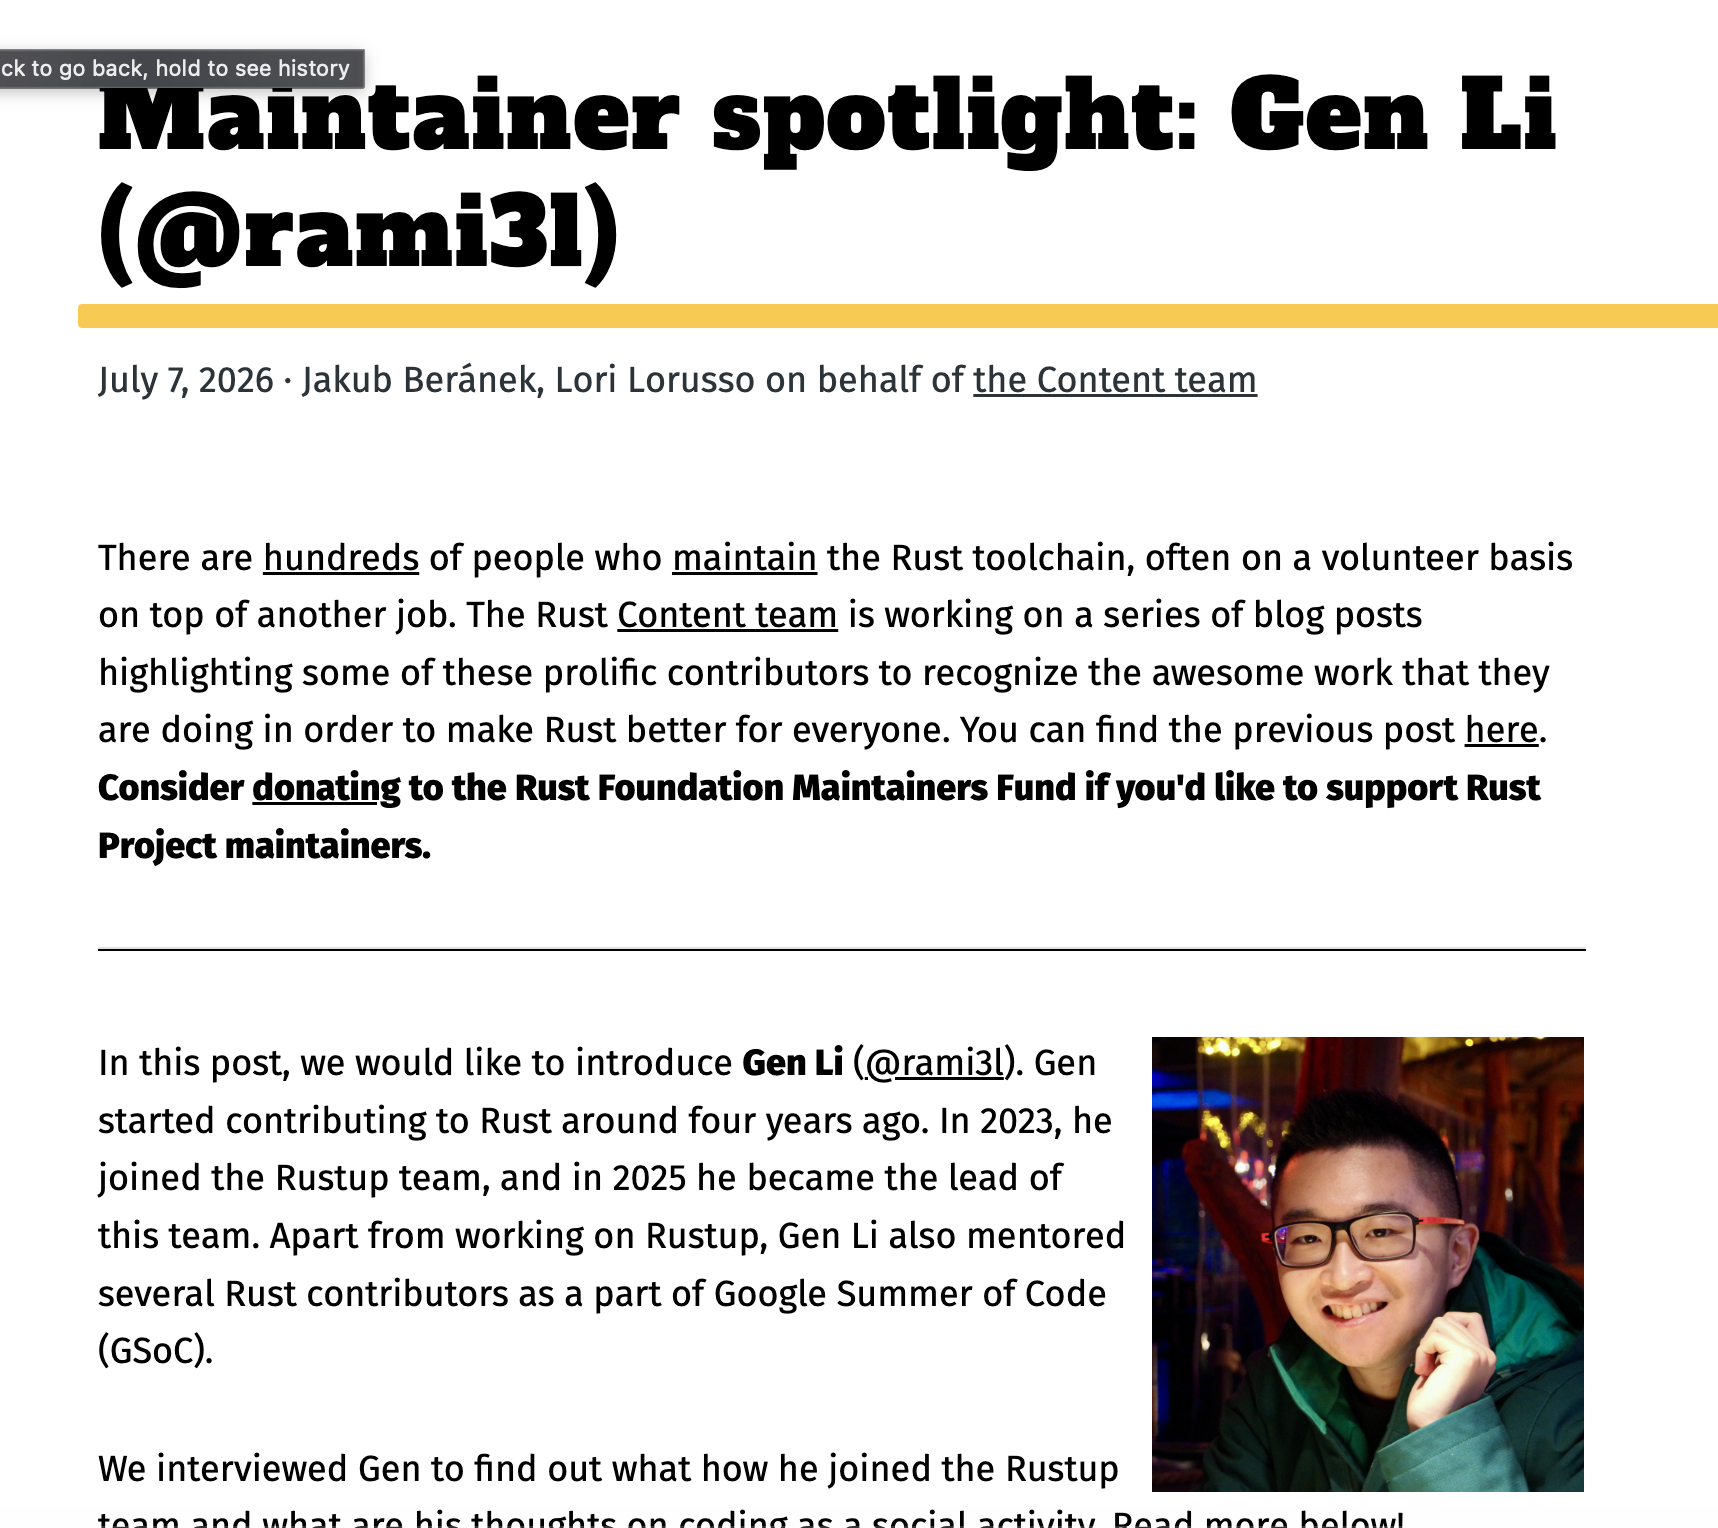
Maintainer spotlight: Gen Li (@rami3l)
>> Gen Li (@rami3l), Rustup team lead since 2025, shares his 4-year Rust journey, tooling passion, maintenance work, GSoC mentoring, and open-source insights.
Alt...
Image: Maintainer spotlight: Gen Li (@rami3l)
>> Gen Li (@rami3l), Rustup team lead since 2025, shares his 4-year Rust journey, tooling passion, maintenance work, GSoC mentoring, and open-source insights.
#rustlang #rust
Formant is hiring Frontend Engineer
🔧 #rust #typescript #react #css
🌎 Remote
⏰ Full-time
🏢 Formant
Job details https://jobsfordevelopers.com/jobs/frontend-engineer-at-formant-io-nov-14-2022-38503d?utm_source=mastodon.world&utm_medium=social&utm_campaign=posting
#jobalert #jobsearch #hiring
Chainlink Labs is hiring Solutions Architect - Capital Markets - APAC
🔧 #c #cplusplus #golang #java #python #rust #solidity #swift #blockchain #defi #web3 #solutionsarchitect
🌎 Remote; Hong Kong
⏰ Full-time
🏢 Chainlink Labs
Job details https://jobsfordevelopers.com/jobs/solutions-architect-capital-markets-apac-at-chainlinklabs-com-jul-29-2024-bbaa5f?utm_source=mastodon.world&utm_medium=social&utm_campaign=posting
#jobalert #jobsearch #hiring
Your Rust Service Isn't Leaking — It Could Be the Allocator via @robey https://lobste.rs/s/srmkur #rust
https://pranitha.dev/posts/rust-and-memory-allocators/
Together for a healthier Clippy https://lobste.rs/s/709awc #rust
https://blog.rust-lang.org/inside-rust/2026/07/06/unite-for-clippy/
A Rust-to-Lean verification pipeline with AI provers: An experience report https://lobste.rs/s/g2bzt2 #formalmethods #rust #vibecoding
https://arxiv.org/html/2605.30106
Place Capability Graphs: A General-Purpose Model of Rust’s Ownership and Borrowing Guarantees https://lobste.rs/s/aspeso #plt #rust
https://dl.acm.org/doi/pdf/10.1145/3763122
Leanstral 1.5: Mistrals KI-Modell für formale Beweise ist Open Source
Mistral AI veröffentlicht Leanstral 1.5 unter Apache-2.0-Lizenz. Das Modell löst laut Mistral 587 von 672 Putnam-Aufgaben und findet automatisiert Bugs in Code.
#Automatisierung #IT #KünstlicheIntelligenz #MachineLearning #Mathematik #OpenSource #Rust #news
[New Post] What are zero-sized types in Rust?
https://blog.keltia.net/til-about-zst-in-rust/

I had a chat with Lori Lorusso and Niko Matsakis about the Rust Foundation Maintainers Fund
Funding open source is a huge topic right now, the Rust Foundation has some great ideas. It will be exciting to watch this one grow and evolve
fin: a Jellyfin & Subsonic client for the terminal https://lobste.rs/s/nwptul #show #rust
https://tangled.org/tsiry-sandratraina.com/fin
What Is the BabaDeda Loader? Analysis of a New ClickFix Malware Campaign.
The BabaDeda loader family has undergone significant advancements in its capabilities, particularly in stealth, evasion, and payload flexibility. Discovered during April 2026, this evolved framework continues to conceal malicious payloads within seemingly legitimate installer packages while expanding its functionality. The attack methodology begins with a social engineering exploit known as ClickFix, which encourages users to execute commands via trusted operating system utilities. This initial step transitions into a sophisticated multi-stage loader that employs several tactics, including hidden PowerShell commands, in-memory shellcode, DLL sideloading, and external payload storage.
Pulse ID: 6a47b2cc64d3d9241377df01
Pulse Link: https://otx.alienvault.com/pulse/6a47b2cc64d3d9241377df01
Pulse Author: AlienVault
Created: 2026-07-03 13:02:04
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#CyberSecurity #ICS #InfoSec #Malware #OTX #OpenThreatExchange #PowerShell #RAT #Rust #ShellCode #SideLoading #SocialEngineering #bot #AlienVault
Jam Programming Language https://lobste.rs/s/r0xrm0 #programming #rust #zig
https://rapha.land/jam-programming-language/
PamStealer: a Rust-based macOS infostealer that validates credentials through PAM
Pulse ID: 6a4b459328d25bbdc8b77726
Pulse Link: https://otx.alienvault.com/pulse/6a4b459328d25bbdc8b77726
Pulse Author: Tr1sa111
Created: 2026-07-06 06:05:07
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#CyberSecurity #InfoSec #InfoStealer #Mac #MacOS #OTX #OpenThreatExchange #Rust #bot #Tr1sa111
Branded Gambling Campaigns: How Scammers Are Exploiting Trusted Brand Names to Drive Casino Traffic
Pulse ID: 6a4b461c2fc6412449dbc361
Pulse Link: https://otx.alienvault.com/pulse/6a4b461c2fc6412449dbc361
Pulse Author: Tr1sa111
Created: 2026-07-06 06:07:24
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#CyberSecurity #InfoSec #OTX #OpenThreatExchange #Rust #bot #Tr1sa111
Announcing the July #Bangalore #FPIndia #Meetup!
When: 1st August (yep 😆)
CFP is open: https://hasgeek.com/fpindia/bangalore-fp-july-2026-meetup
Come meet fellow FP heads, have great conversations, all skill levels welcome!
#PureScript #Typescript #Rust #Erlang #Scala #OCaml #FunctionalProgramming
A Novel Look at Error Handling in Rust https://lobste.rs/s/l0yqco #rust
https://jtjlehi.github.io/2026/06/25/novel-rust-error-handling.html
Work In Progress Rust https://lobste.rs/s/qu1bwq #practices #rust
https://blog.dureuill.net/articles/wip/

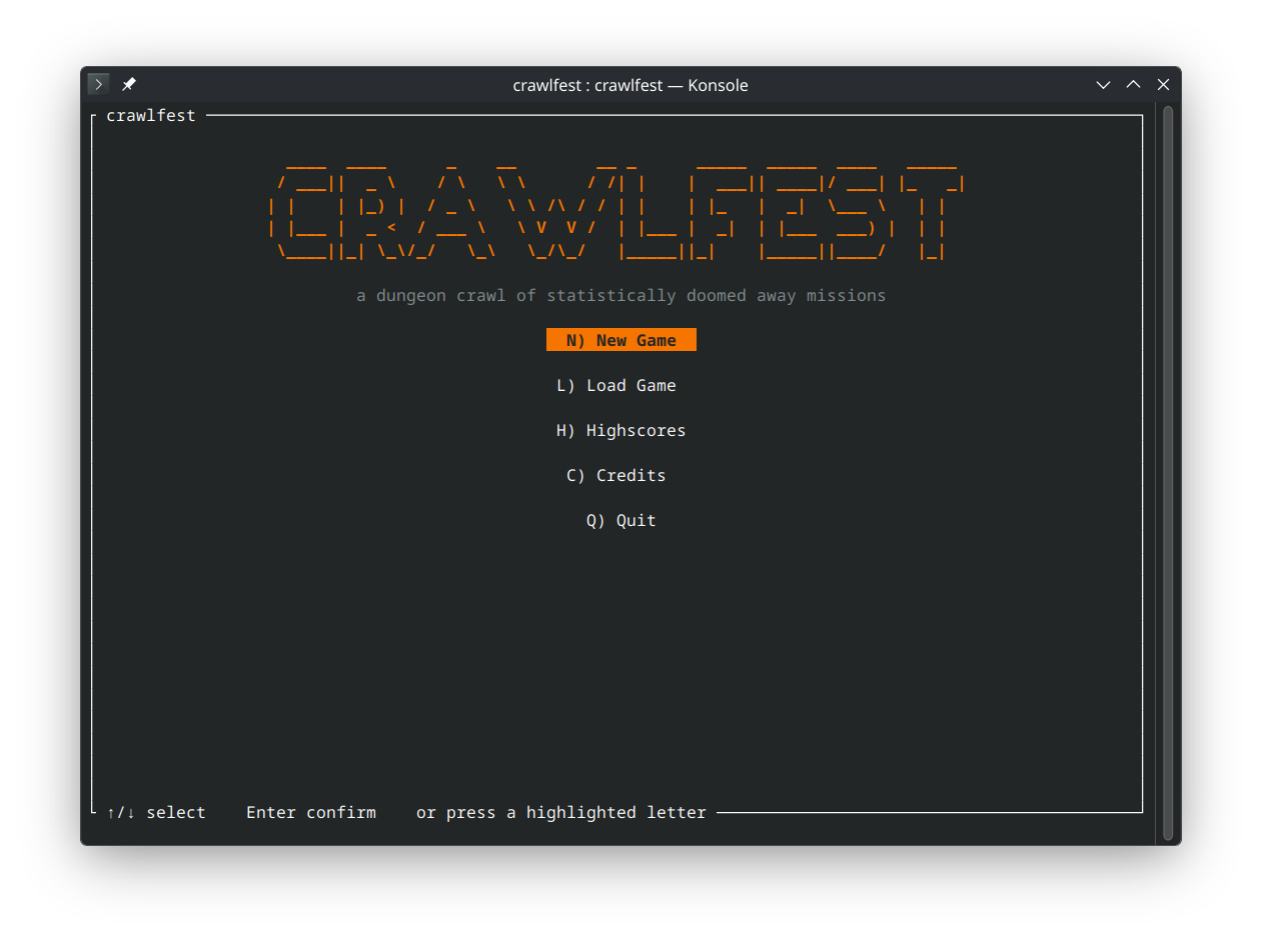
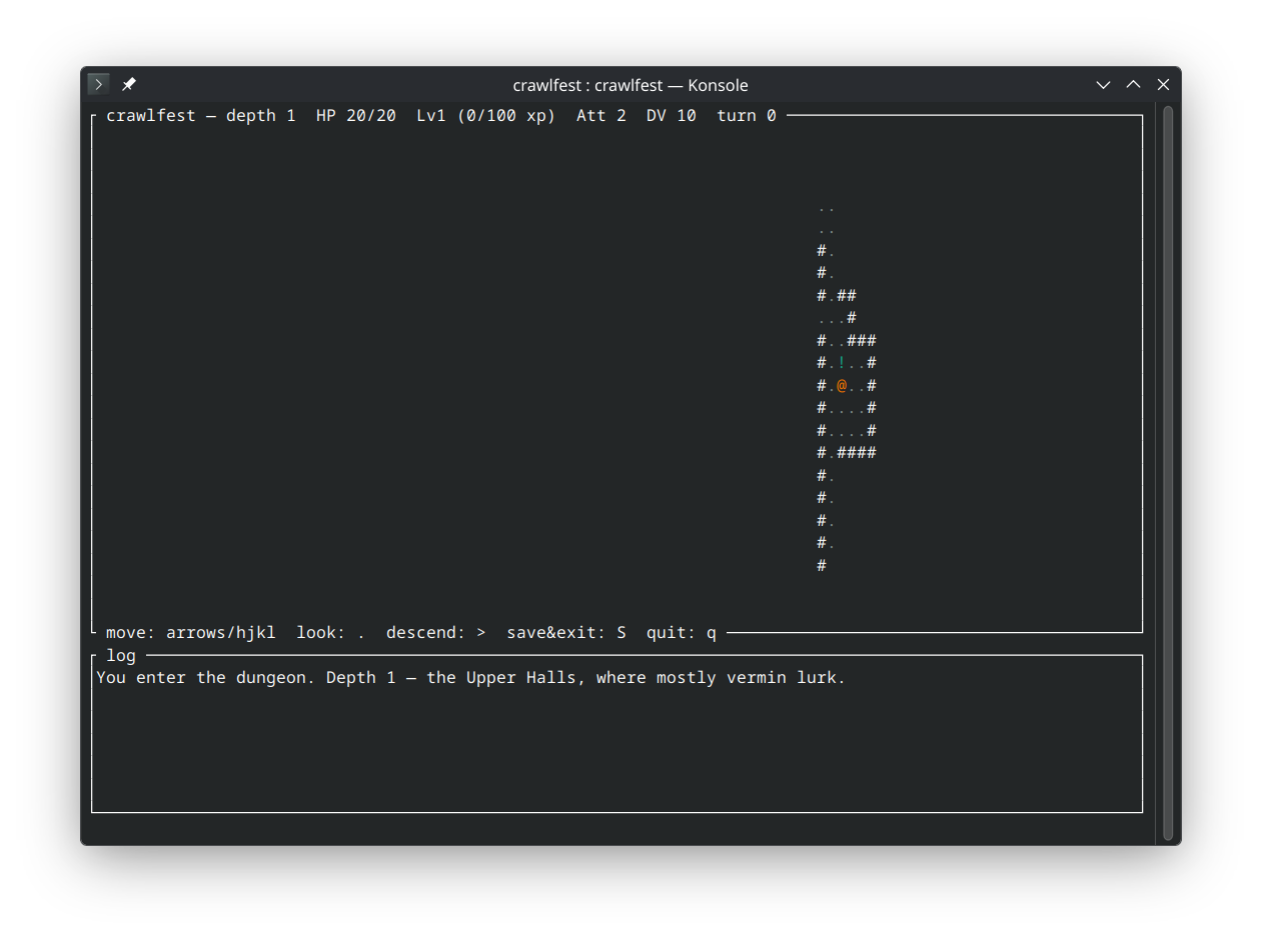
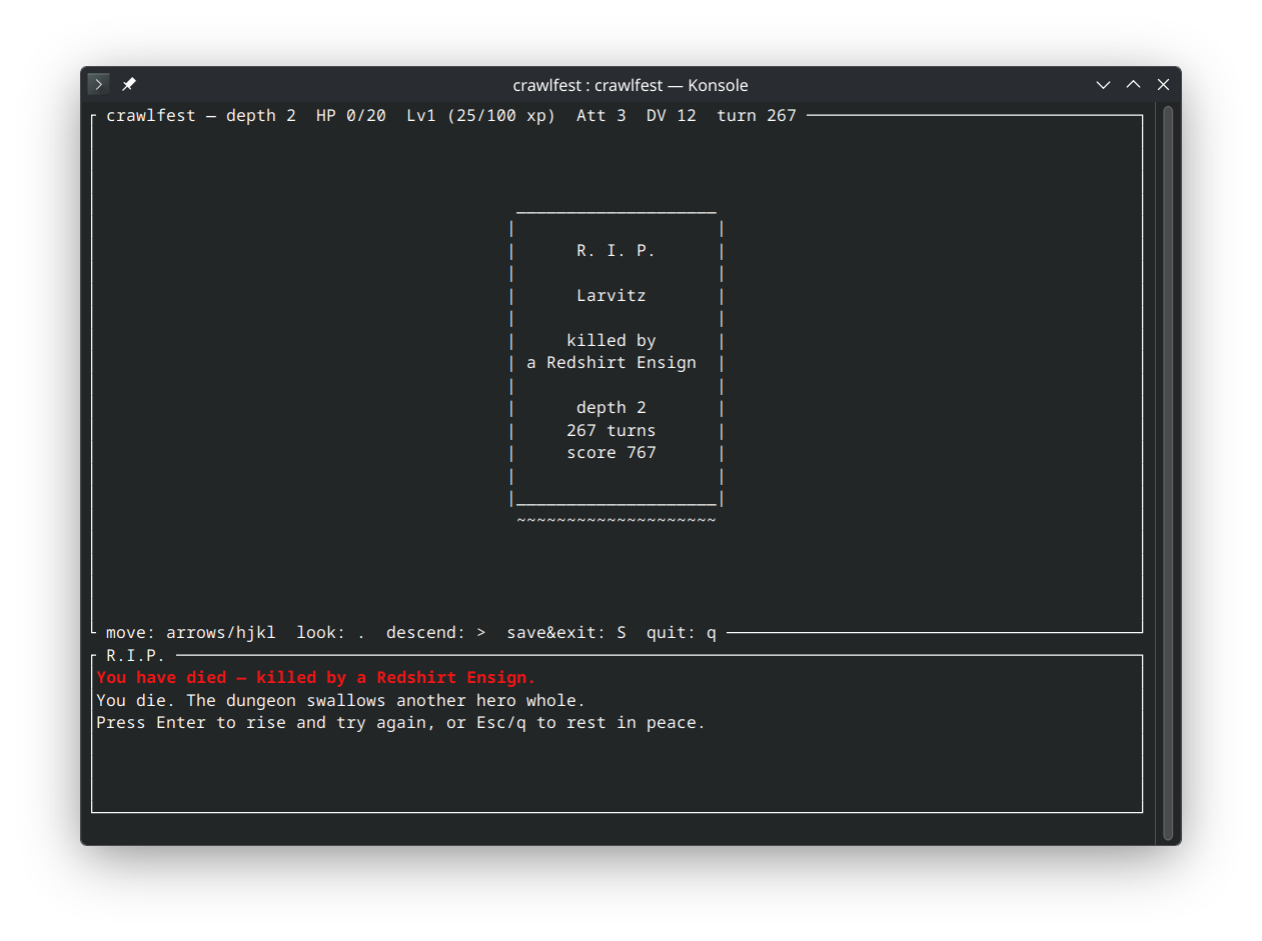
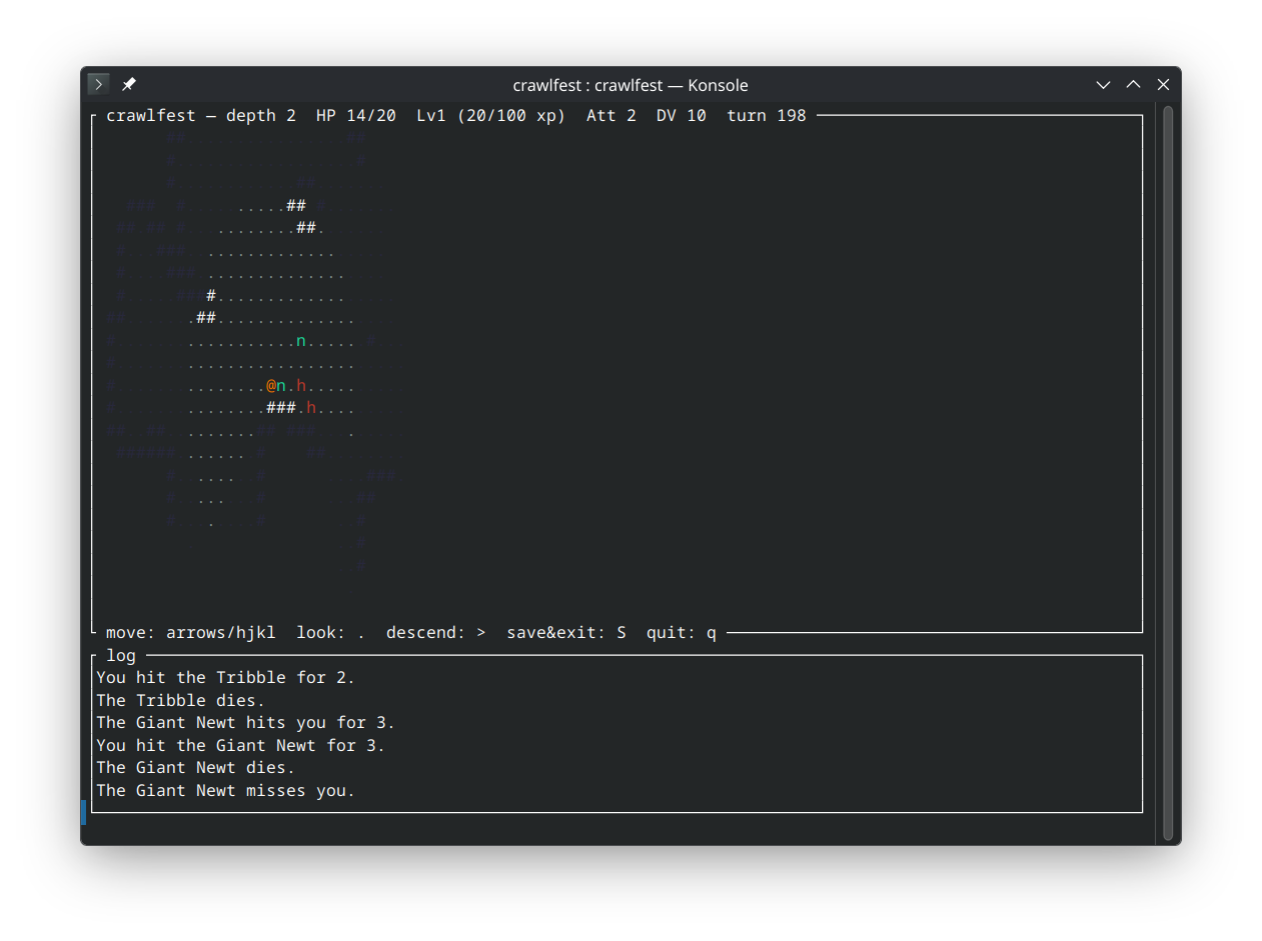
My Roguelike game starts feeling better and better :-) So much fun building it out further and further every weekend 🙂
Implemented better save-state handling, combat machenics including weapons and armor, cavernous levels and much more this weekend. YAY.
#gamedev #roguelike #rust #development
Threat Campaign Exploits Trusted Brands To Drive Casino Traffic
Campaign uses affiliate programs for their income and AI generated promotional videos filmed to look like they were shot outside real brand locations, featuring fake employees and authentic branding.
Pulse ID: 6a4a4a572e629b931648c641
Pulse Link: https://otx.alienvault.com/pulse/6a4a4a572e629b931648c641
Pulse Author: cryptocti
Created: 2026-07-05 12:13:11
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#CyberSecurity #InfoSec #OTX #OpenThreatExchange #RAT #Rust #bot #cryptocti
Is your company currently hiring for a role that includes using Rust?
Reply with a link to the opening and any relevant context.
If you're not, we'd appreciate a repost for visibility
Rust - Handling Results In A Map Closure via @bd103 https://lobste.rs/s/1r09vz #practices #rust
https://reemus.dev/tldr/rust-handling-results-in-map-closure

A Windows Kernel in a Browser Tab, Part I: Cold Boot, Fast Boot, and Four Megabytes:
https://www.msuiche.com/posts/nanokrnl-cold-boot-fast-boot/
#kernel #infosec #programming #rust #windows #hacking
Alt...
A Windows Kernel in a Browser Tab, Part I: Cold Boot, Fast Boot, and Four Megabyte

Day 5, a picture worth a thousand words 👇
I put an API-breaking `#[doc(hidden)]` in my local build of the Rust standard library, and asked cargo-semver-checks to find it. See for yourself!

Alt...
cargo-semver-checks output where the "function now doc hidden" lint is triggered, warning that the "black_box" function in library/core/src/hint.rs is now #[doc(hidden)] and no longer public API. The run took 6.7s total.

Gaslight macOS Backdoor Uses Prompt Injection on LLMs
🔗 https://cybersecurefox.com/en/gaslight-macos-rust-backdoor-prompt-injection

 domenuk
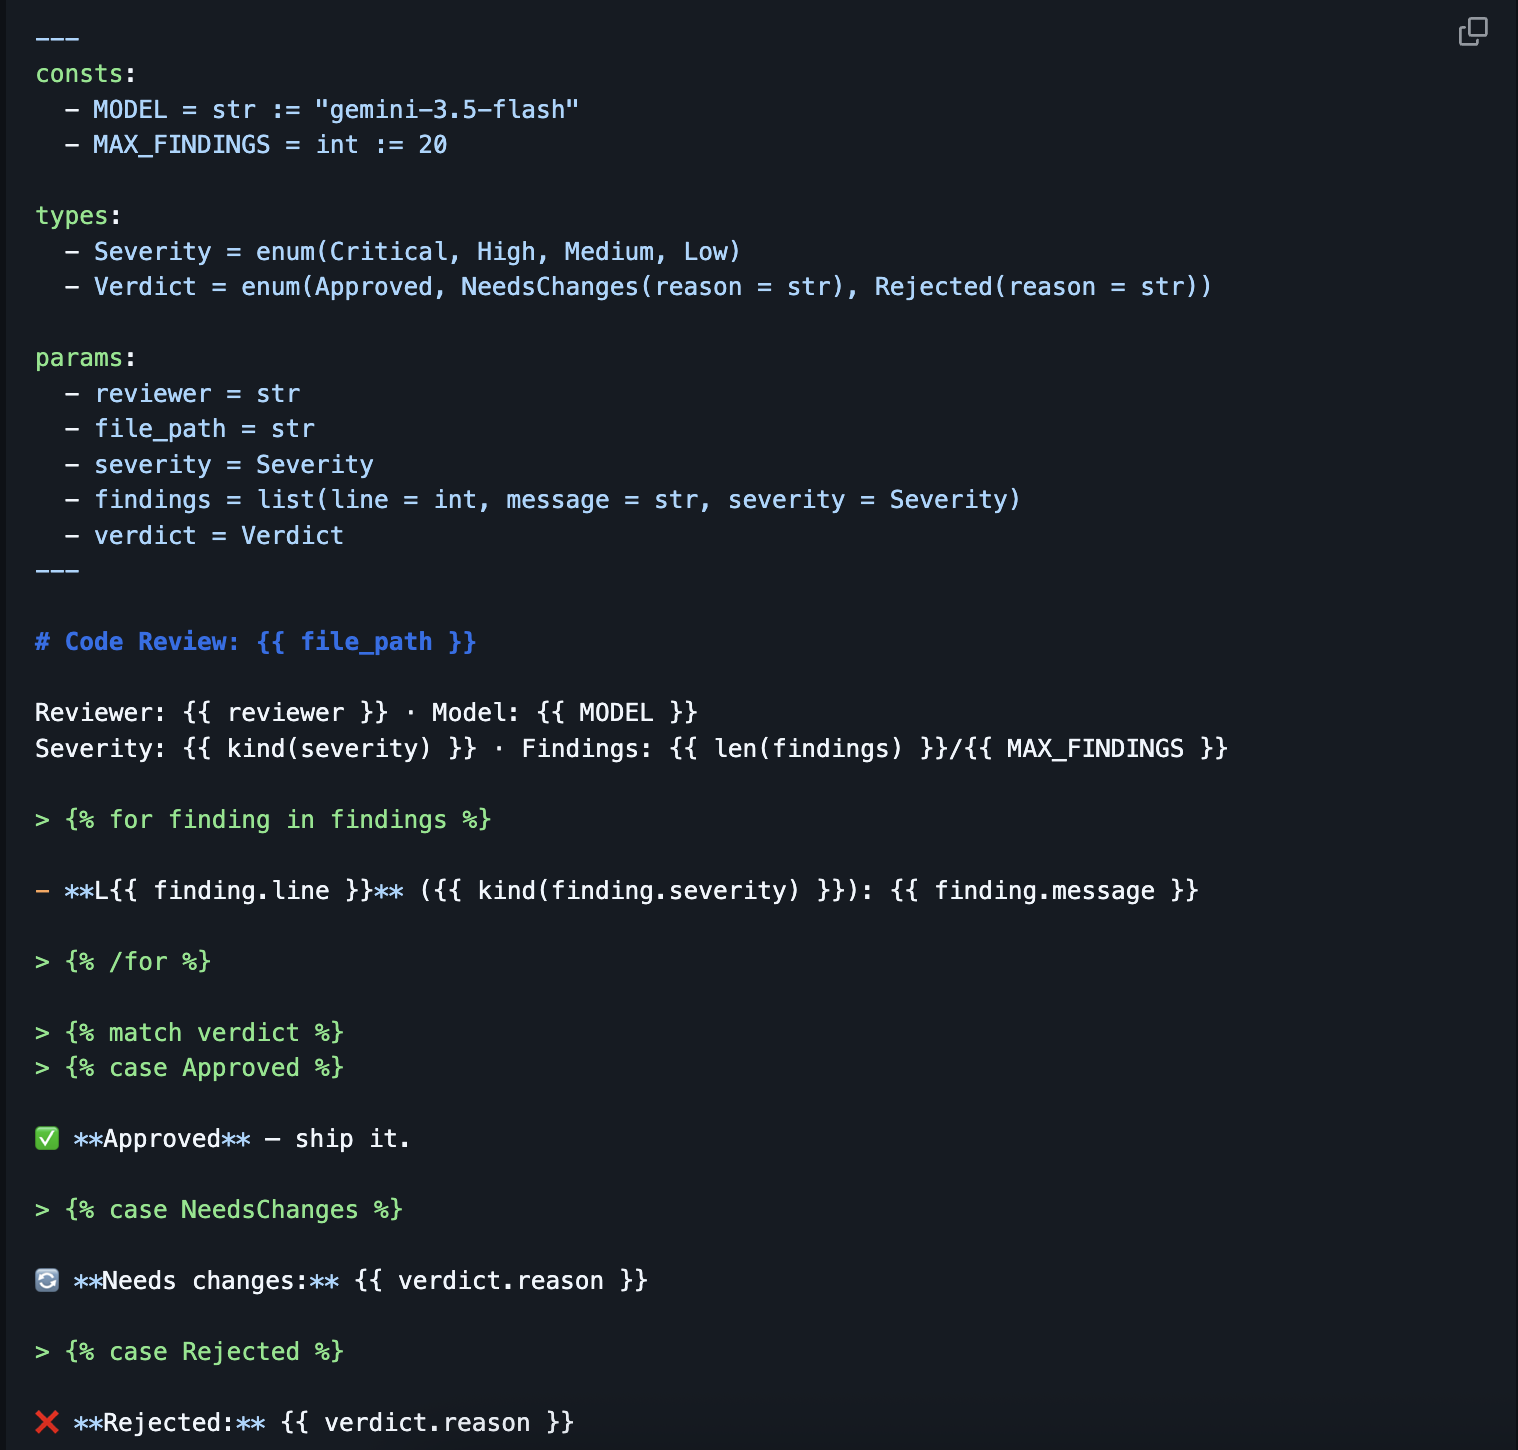
If you're writing agents, you can now use strongly-typed markdown templates.
Like, declare what types your template/prompt expects, check at compile time, for #rust, #go, #python, #typescript ...
(things you didn't know you needed :P)
https://github.com/domenukk/md-tmpl
#agents #prompts #overengineering
Alt...
An example of how to use md-tmpl - a nice looking way of declaring params and types in frontmatter, then using them in the markdown below.
----------------
🦠 Malware Analysis
===================
KuinaExtractor: Six Months of a Rust Infostealer's Evolution
ThreatRay published a detailed analysis tracking a Rust-based infostealer family across four major build iterations and two parallel experiments from December 2025 through June 2026.
December 2025 — First Build
The earliest builds were already full-featured: Chrome v20 App-Bound-Encryption bypass via LSASS impersonation for master key recovery, theft of Roblox cookies, Steam sessions, crypto wallets, and Discord tokens. Exfiltration used a Discord webhook. Privilege escalation relied on a single fodhelper/ms-settings UAC bypass. GitHub served as both CDN and disposable VPS/RDP infrastructure via GitHub Actions.
January 2026 — Rewrite
A rapid rebuild added substantial reconnaissance: eight WMIC hardware queries, WiFi SSID enumeration, Windows Credential Manager dump, a routine terminating 17 browser processes, victim-IP geolocation, and a loop disabling Microsoft Defender. Exfiltration shifted to a Telegram bot. The single UAC bypass was replaced by a function-pointer table with seven methods.
March 2026 — Production Hardening
The cookie-theft mechanism remained (LSASS/ABE chain, extended with ChaCha20-Poly1305 for newer Chrome versions). UAC bypass moved to SilentCleanup. Browser coverage grew to roughly 40 targets including CocCoc. Broad VM and sandbox detection was added. This variant is still observed today.
June 2026 — "k0to" Rebrand
The build dropped the "Kuina" name and shifted focus to concealment. It uses a self-contained HTTP stack (reqwest over hyper and rustls) with its own CA roots, 28-byte XOR string wrapping including the Telegram C2 URL, and scans PowerShell window titles for analyst tools. The Telegram channel is push-only.
Parallel Experiments
• KuinaCookieExtractor (January): Leaner codebase, Discord webhook exfiltration, lighter anti-analysis (logs VM warning and continues). Linked to same author via kuina build user, KUINA_UAC_BYPASS_ATTEMPTED sentinel, and kuina1999 handle. Disappeared after two weeks.
• Zenith (April-May): Short-lived C2 experiment. Debug build shipped with verbose [DEBUG] traces to zenith_debug.txt, including author self-attribution. Mutex disguised as network adapter name. Panel at 103.229.53[.]18:3000 (Vietnamese AS135918). Abandoned within days.
The developer iterates quickly and learns from deployment feedback. The self-contained TLS stack and XOR wrapping in k0to indicate awareness of network-based detection signatures.
🔹 KuinaExtractor #infostealer #malware_analysis #Rust #threat_intelligence
🔗 Source: https://www.threatray.com/blog/kuinaextractor-six-months-of-a-rust-infostealers-evolution
Branded Gambling Campaigns: How Scammers Are Exploiting Trusted Brand Names to Drive Casino Traffic
Scam advertising campaigns have been identified that impersonate trusted brands to redirect consumers to unrelated online gambling sites. These operations utilize paid social media advertisements on platforms like Facebook, Instagram, and TikTok, combined with fake app store pages and Progressive Web Apps. The campaigns target UK consumers primarily, with variants observed in German and Spanish. Scammers impersonate major brands including financial institutions like Monzo, Revolut, and Barclays, as well as household names such as Tesco, Amazon, Netflix, and Facebook. The scheme involves three stages: paid ads claiming brands have launched official casino products, fake landing pages mimicking app stores, and PWAs that redirect to gambling sites through affiliate tracking links. Typical affiliate payouts range from $50 to $350 per depositing player, indicating significant financial motivation behind these operations.
Pulse ID: 6a46d12100d65a16f173e8a4
Pulse Link: https://otx.alienvault.com/pulse/6a46d12100d65a16f173e8a4
Pulse Author: AlienVault
Created: 2026-07-02 20:59:13
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#Amazon #CyberSecurity #Facebook #InfoSec #Instagram #Mimic #OTX #OpenThreatExchange #RAT #Rust #SocialMedia #UK #bot #AlienVault
crustc: Entirety of rustc, translated to C https://lobste.rs/s/ryny2c #rust
https://github.com/FractalFir/crustc
Second, an improvement to how we normalize types.
We'll need this to implement type-checking lints in the future. This will eliminate a large class of expensive type-checks where the previous logic was unnecessarily conservative and quite inefficient.
https://github.com/obi1kenobi/trustfall-rustdoc-adapter/pull/1086
It's Thursday, day 4. Today's haul so far is ~2500 LoC.
First, making use of default-value stability which we previously exposed in rustdoc JSON. Pairing with Codex on this caught a subtle new edge case that affects which traits are considered sealed.
Copious test cases come standard, of course.
https://github.com/obi1kenobi/trustfall-rustdoc-adapter/pull/1087
Binance is hiring Smart Contract Security Engineer
🔧 #golang #python #rust #solidity #blockchain #defi #web3 #securityengineer
🌎 Remote; Singapore
⏰ Full-time
🏢 Binance
Job details https://jobsfordevelopers.com/jobs/smart-contract-security-engineer-at-binance-apr-17-2024-c6fd42?utm_source=mastodon.world&utm_medium=social&utm_campaign=posting
#jobalert #jobsearch #hiring
Databricks is hiring Software Engineer - Backend
🔧 #golang #java #rust #scala
🌎 Aarhus, Denmark
⏰ Full-time
🏢 Databricks
Job details https://jobsfordevelopers.com/jobs/software-engineer-backend-at-databricks-com-jul-31-2025-a86e8d?utm_source=mastodon.world&utm_medium=social&utm_campaign=posting
#jobalert #jobsearch #hiring
[$] AURpocalypse now: a look at the recent AUR attacks
The Arch User Repository (AUR) has been subjected to a sustained attack recently. The attacker, or attackers, have spun up a series of new accounts then used them to adopt orphaned [...]
https://lwn.net/Articles/1077619/ #LWN #Linux #ArchLinux #Rust #Git #Firefox
A single RedLine C2 pivots into a maritime spear-phishing cluster and attacker-owned infrastructure.
An investigation beginning with a single RedLine Stealer C2 server from VMRay UniqueSignal evolved into uncovering a targeted Business Email Compromise campaign against South Korean maritime infrastructure. The analysis started with IP 194.156.79.122 on port 55615, leveraging fingerprinting techniques through FOFA and VirusTotal to identify additional C2 infrastructure. Pivoting through communicating files revealed spear-phishing emails targeting Kangrim Heavy Industries, a major South Korean marine boiler manufacturer. The campaign delivered Formbook malware through impersonated maritime supply chain companies. Further infrastructure analysis identified seven fraudulent domains hosted on TheHost LLC infrastructure, utilizing similar naming patterns and TLS certificates. The attack demonstrates sophisticated BEC tactics combining malware delivery with social engineering, mimicking legitimate business correspondence within the maritime shipping sector.
Pulse ID: 6a464b96bef17724be5668a0
Pulse Link: https://otx.alienvault.com/pulse/6a464b96bef17724be5668a0
Pulse Author: AlienVault
Created: 2026-07-02 11:29:26
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#CyberSecurity #Email #FormBook #ICS #InfoSec #Korea #Malware #Mimic #OTX #OpenThreatExchange #Phishing #RAT #RedLine #RedlineStealer #Rust #SocialEngineering #SouthKorea #SpearPhishing #SupplyChain #TLS #VirusTotal #bot #AlienVault
ClickHouse is hiring Senior Software Engineer - JVM Language Clients
🔧 #csharp #cplusplus #golang #java #javascript #python #rust #api #kafka #sql #seniorengineer
🌎 Remote; Canada
⏰ Full-time
🏢 ClickHouse
Job details https://jobsfordevelopers.com/jobs/senior-software-engineer-jvm-language-clients-at-clickhouse-com-apr-22-2026-f7438d?utm_source=mastodon.world&utm_medium=social&utm_campaign=posting
#jobalert #jobsearch #hiring