Search results for tag #rust
Cylic trait implementations: motivation https://lobste.rs/s/zq9czz #compilers #plt #rust
https://smallcultfollowing.com/babysteps/blog/2026/08/10/cyclic-trait-solving/
RangeFrom, Part 1․․ https://lobste.rs/s/xgnakx #historical #rust
https://erk.dev/2026/08/12/rangefrom-part-1
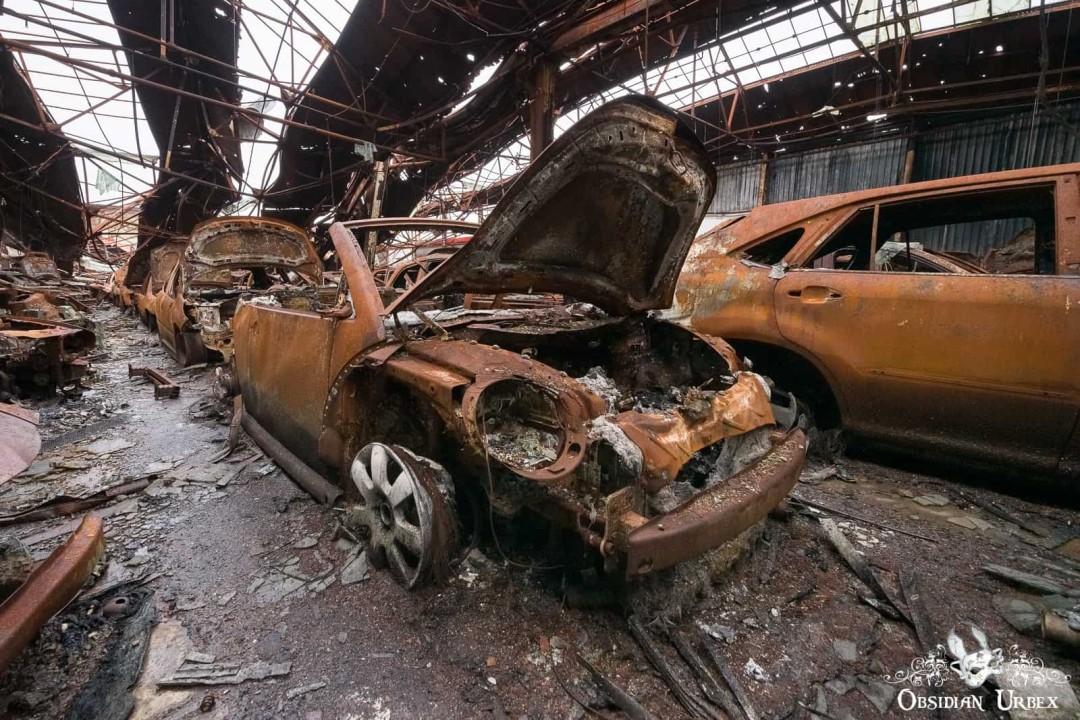
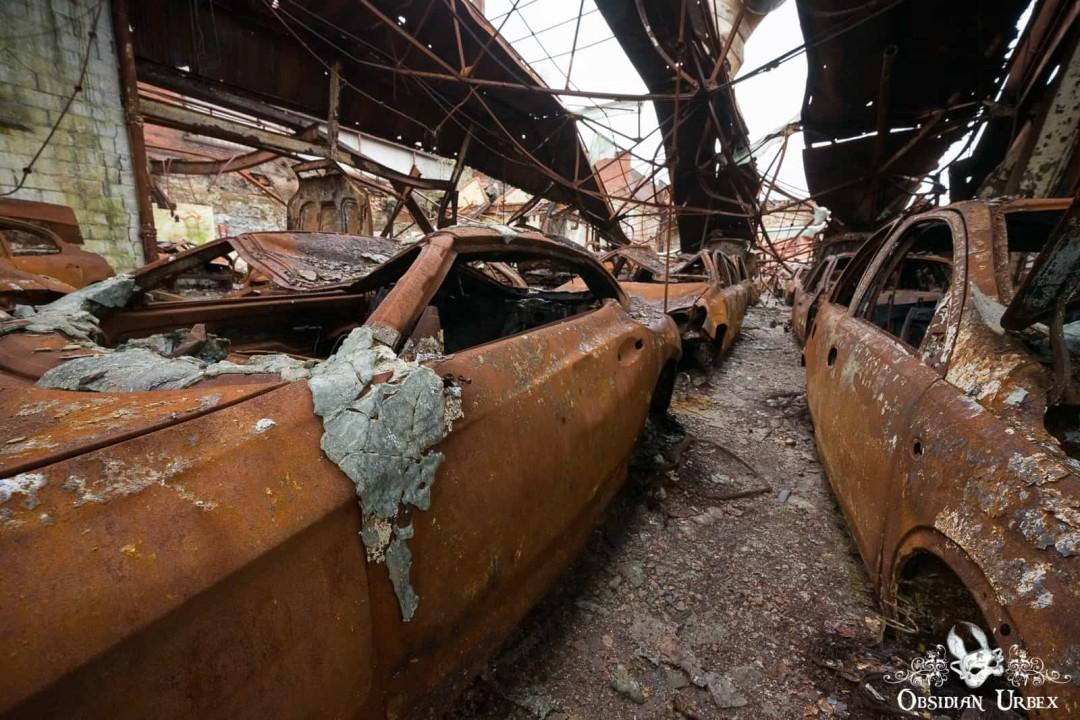
This burnt-out car dealership, Preston. It looks like a post-apocalyptic scene from the #Fallout series. Twisted car shells and orange oxidised metal fill the collapsed warehouse.
Approximately 150 vehicles were inside when the fire started. Heat melted window glass, which pooled across the floor. Investigators confirmed the fire was an arson attack. A few months after my visit, the site was cleared.
#PostApocalyptic #Rust #Urbex #Photography #Fire #WeirdCarMastodon #Ruins
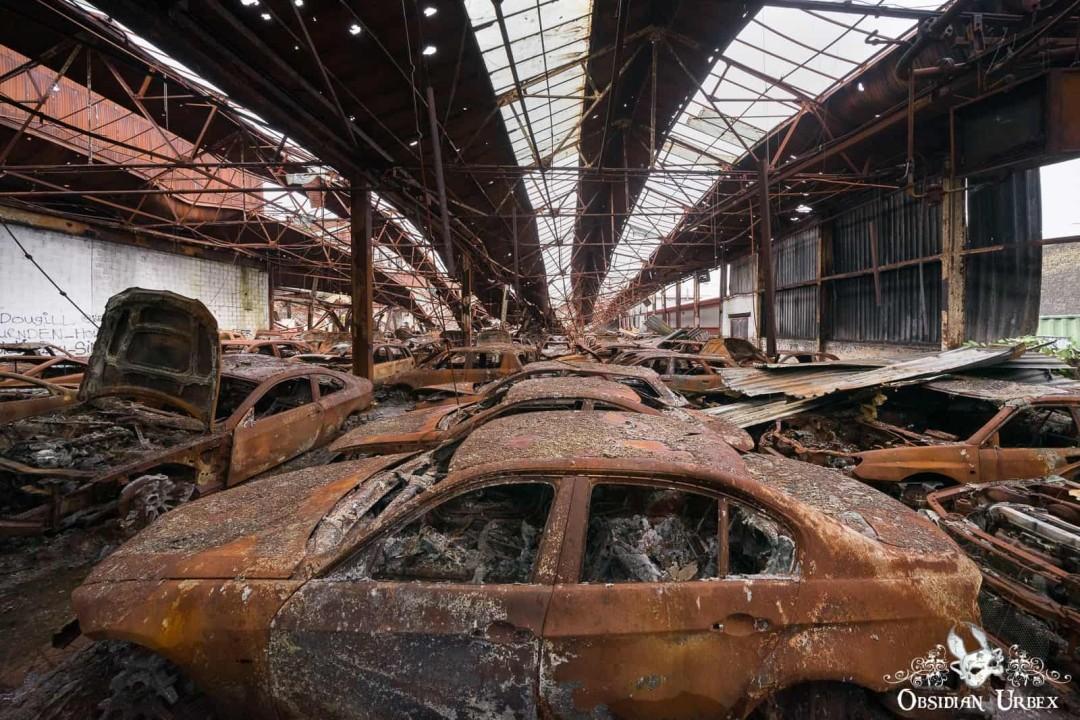
Alt...
A desolate, fire-damaged car dealership. Rows of burnt, rusted cars fill the ruined warehouse under a partially collapsed roof
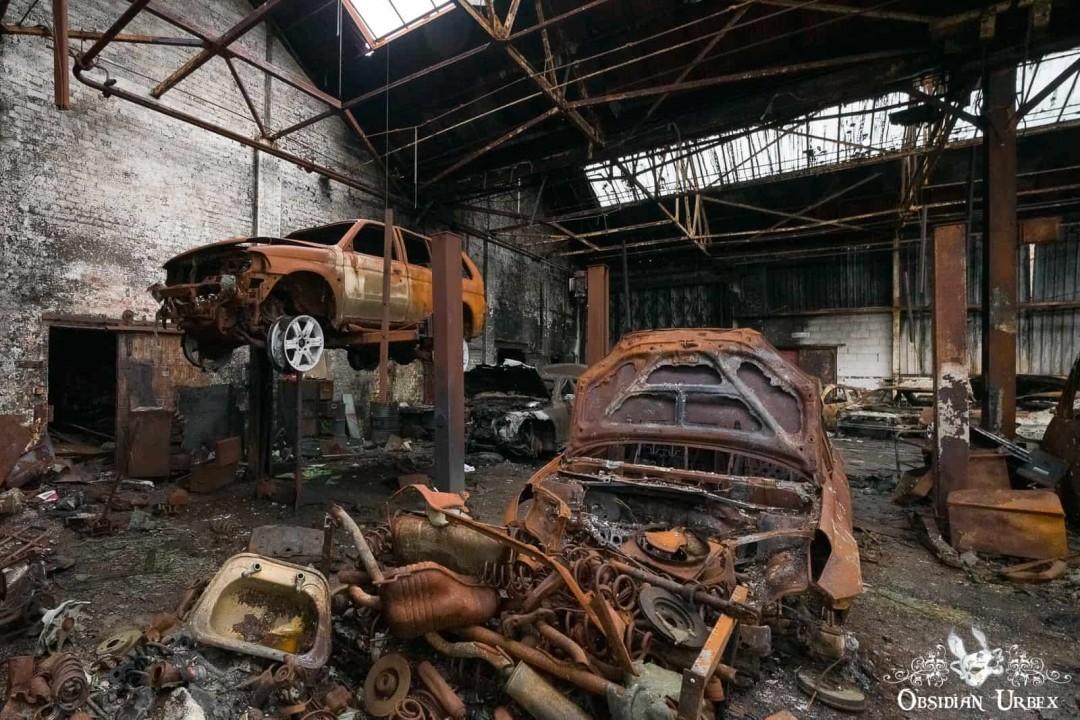
Alt...
An abandoned, fire-damaged car dealership features a rusty car on a lift amidst charred vehicle wreckage.
Alt...
Burnt out VW Beetle
Alt...
Rows of burnt cars, the glass has melted and slumped down from the car windows

.
#urbansketchers #urbansketching #sketchbook #rust #industriesalon #mixedmedia

Alt...
An open sketchbook with a drawing of an old industrial rail transport thingy at Industriesalon Schöneweide.

Alt...
The original old and rusty industry rail transport thingy.

Alt...
Berlin urban sketchers throwdown, lots of sketchbooks on the floor.
MongoDB is hiring Security Software Engineer, Infrastructure Security (Staff or Senior)
🔧 #c #cplusplus #golang #java #python #rust #aws #azure #cicd #gcp #kubernetes #mongodb #terraform #securityengineer #seniorengineer
🌎 Austin, Texas; San Francisco, California; Seattle, Washington; United States
⏰ Full-time
🏢 MongoDB
Job details https://jobsfordevelopers.com/jobs/security-software-engineer-infrastructure-security-staff-or-senior-at-mongodb-com-mar-26-2026-e00c1b?utm_source=mastodon.world&utm_medium=social&utm_campaign=posting
#jobalert #jobsearch #hiring
Bevy's Sixth Birthday https://lobste.rs/s/oppmip #games #rust
https://bevy.org/news/bevys-sixth-birthday/
Mozilla is hiring Senior Security Engineer, Bug Bounty
🔧 #golang #javascript #python #rust #aws #azure #gcp #securityengineer #seniorengineer
🌎 Remote; Germany
⏰ Full-time
🏢 Mozilla
Job details https://jobsfordevelopers.com/jobs/senior-security-engineer-bug-bounty-at-mozilla-org-aug-2-2026-fbf5d2?utm_source=mastodon.world&utm_medium=social&utm_campaign=posting
#jobalert #jobsearch #hiring
Note to self, and anybody that has the gumption to try.
When making a port on #freebsd that utilizes massive dependencies, like #rust #gcc or #llvm do not tell #poudriere to use the latest branch for fetching dependencies from pkg. The local install of pkg must be newer or the same as the one used in the jail.
Restricting trait implementability and field mutability https://lobste.rs/s/9j3n3b #rust
https://blog.rust-lang.org/inside-rust/2026/08/10/call-for-testing-impl-and-mut-restrictions/

Just dropped v1.0.2 of Audio Tetris... Did some refining of the menu system, fixed some bugs with muting and switching background music tracks and look at that, you can now save your games in progress. Also there's a scoreboard of sorts. Download your copy here: https://github.com/thegregariousdragon/audio-tetris/releases/tag/v1.0.2 #A11Y #Accessibility #Blind #AudioGame #Tetris #Rust #WxDragon
We're not done with point clouds https://lobste.rs/s/ctwrrt #performance #rust
https://claytonwramsey.com/blog/mvt/

Blazingly Fast or Blazingly Hyped? A Reality Check on Rewriting in Rust
#RustLang #Rust #Rustrover #Rewritinginrust #Riir
https://blog.jetbrains.com/rust/2026/08/10/rewriting-in-rust/

RE: https://chaos.social/@ponygol/117071279449204535
#Rust finally gets asymmetric visibility, two years after #PHP added it.
Boo. Yah.
Greatness PhaaS Steals Microsoft 365 Tokens Despite MFA
The Greatness Phishing-as-a-Service platform uses Adversary-in-the-Middle
and device-code phishing to steal Microsoft 365 authentication tokens and
bypass MFA. Active campaigns exploit trusted sender configurations and
phishing lures to compromise accounts. Stolen tokens enable attackers to
access Outlook, Teams, SharePoint and OneDrive while evading
conventional authentication-based security controls.
Pulse ID: 6a79bef48cee5cb15fd34fd2
Pulse Link: https://otx.alienvault.com/pulse/6a79bef48cee5cb15fd34fd2
Pulse Author: cryptocti
Created: 2026-08-10 12:07:16
Be advised, this data is unverified and should be considered preliminary. Always do further verification.
#AdversaryInTheMiddle #CyberSecurity #EDR #InfoSec #MFA #Microsoft #OTX #OpenThreatExchange #Outlook #Phishing #RAT #Rust #bot #cryptocti

Чудовий, здоровий погляд на використання великих мовних моделей (ВММ a.k.a. ШІ) від автора політики щодо ВММ проєкту Rust. Думаю, це можна застосувати не тільки до розробки софту. Я радий знати, що спільнота проєкту Rust дивиться на це саме таким чином.
Загалом, ця політика зосереджена на розумінні і сприянні у тому, щоб у нас була ментальна модель нашого коду, а не лише артефакти, які механічно виконують правильні дії.
Основне питання – довкола чого і яких цінностей люди збираються разом, щоб працювати над проєктом, що́ вони хочуть спільно накопичувати й будувати, і що очікують одне від одного, а не у тому, добрий чи поганий код геренують ВММ per se.
Думаю, більшість авторів пропозицій (змін до) коду, які використовують ВММ, переконані, що вони щиро допомагають, але для нас сам код є найменшою, і в певному сенсі найменш важливою частиною пропонованих змін. Нас значно більше хвилює те, чи розуміє автор/ка, що́ цей код робить, чи роздумує він/вона над тим, як цей код буде змінюватися у майбутньому, і чи приймає усвідомлені рішення про те, як цей код має виглядати. Сам по собі код ніяк не сприяє жодній з цих речей.
Тобто ціннішою за код є когнітивна участь, усвідомлене прийняття рішень людиною по той бік екрану. Код завжди можна переписати, але цього неможливо зробити без достатнього розуміння самої проблеми, того, як саме ми її вирішуємо, і як це рішення буде жити довготерміново.
Ми часто зіштовхумося з ситуацією, коли людина відповідає на коментар, копіюючи його у ВММ і вставляючи назад її відповідь. Скажу прямо: це марна трата часу усіх залучених. Якщо б нам була потрібна відповідь ВММ, ми б самі запитали. Ми хочемо почути вашу думку, а не думку машини.
Мене турбує асиметрія зусиль і відповідальності, яка тут виникає: той, хто називає себе автором, з допомогою машини дуже швидко створює щось, що потім хтось інший має повністю «перетравити» і зрозуміти, щоб приймати усвідомлені рішення і відповідати за це перед кінцевими користувачами і всіма іншими учасниками проєкту.
Ще з давніх до-ШІшних часів я пригадую, як мене дратувало зловживання машинним перекладом окремими авторами в українській Вікіпедії, а особливо коли це ще й було порушенням авторського права (я нерідко вилучав такий переклад). Мені здається, тут щось подібне – нагенерувати щось машиною можна швидко, але хто буде за це відповідати? Хто хоча б раз уважно прочитає це повністю, перш ніж віддавати іншим?
Недавно спостерігав, як один розробник зіштовхнувся з нагенерованою ВММ пропозицією змін до свого проєкту. Кінець кінцем він просто переробив все самостійно. Не тому, що код був якимось докорінно неправильний, а тому що це був не той код, який він хотів бачити в своєму проєкті («хто таке пише?»), і він не бачив сенсу казати про це «автору»:
Це важливо не тому, що я не готовий прийняти код, створений ВММ. Але через це мені складно зрозуміти, чи є сенс писати автору мої побажання щодо коду, чи простіше переробити це самому.
Тобто проблема не стільки в самому коді, скільки у способі взаємодії і очікуваннях одне від одного.
Також тут виникає ряд інших етичних питань – наприклад, якщо людина створила з мінімальними зусиллями 100 пропозицій коду з допомогою ВММ, 25 з яких потім опрацювали і довели до пуття інші (решту 75 викинули), а потім ця сама людина в своєму CV подасть список з цих 25 змін як своє індивідуальне досягнення – наскільки це чесно?
Ніхто крім автора не зобов'язаний читати вивід ВММ, за винятком добровільного вибору: вивід ВММ заборонений в публічній документації, описах пропозицій змін, а також коментарях на GitHub, якщо він не є явно промаркований¹. Рецензенти не зобов'язані читати ВММні пропозиції змін, якщо вони не бажають.
Вважаю, що це чудовий принцип – він відразу чітко декларує рівень очікуваної залученості інших до створеного кимось ВММного вмісту, на противагу вмісту, артикульованого самою людиною безпосередньо.
Ви можете генерувати ВММ-ний вміст, якщо тільки ви його бачите, без розкриття [факту використання ВММ], поки ви не публікуєте його де-небудь з очікуванням, що ми будемо його читати чи рецензувати.
Це справедливо.
При тому зверніть увагу, що політика не містить категоричної заборони на використання ВММ для генерування самого коду:
Узгоджений заздалегідь, некритичний, високоякісний, добре відтестований і добре відрецензований код, який початково був створений ВММ, дозволяється, з розкриттям [факту використання ВММ].
Отже, це не проблема коду самого по собі, а питання презумпцій щодо того, наскільки кожен/на з учасників залучені когнітивно. Код, який потрапляє до користувачів і еволюціонує, стає кращим і якіснішим протягом десятиліть, – це вже результат усієї цієї взаємодії і інвестованого спільного [когнітивного] капіталу.
🐨
--
¹ Останнє стосується тільки коментарів на GitHub.
Circle is hiring Principal Security Engineer, Security
🔧 #golang #rust #solidity #blockchain #web3 #aws #cicd #gcp #json #principalengineer #securityengineer
🌎 Remote; San Francisco, California; United States
⏰ Full-time
🏢 Circle
Job details https://jobsfordevelopers.com/jobs/principal-security-engineer-security-at-circle-com-sep-10-2024-944bde?utm_source=mastodon.world&utm_medium=social&utm_campaign=posting
#jobalert #jobsearch #hiring
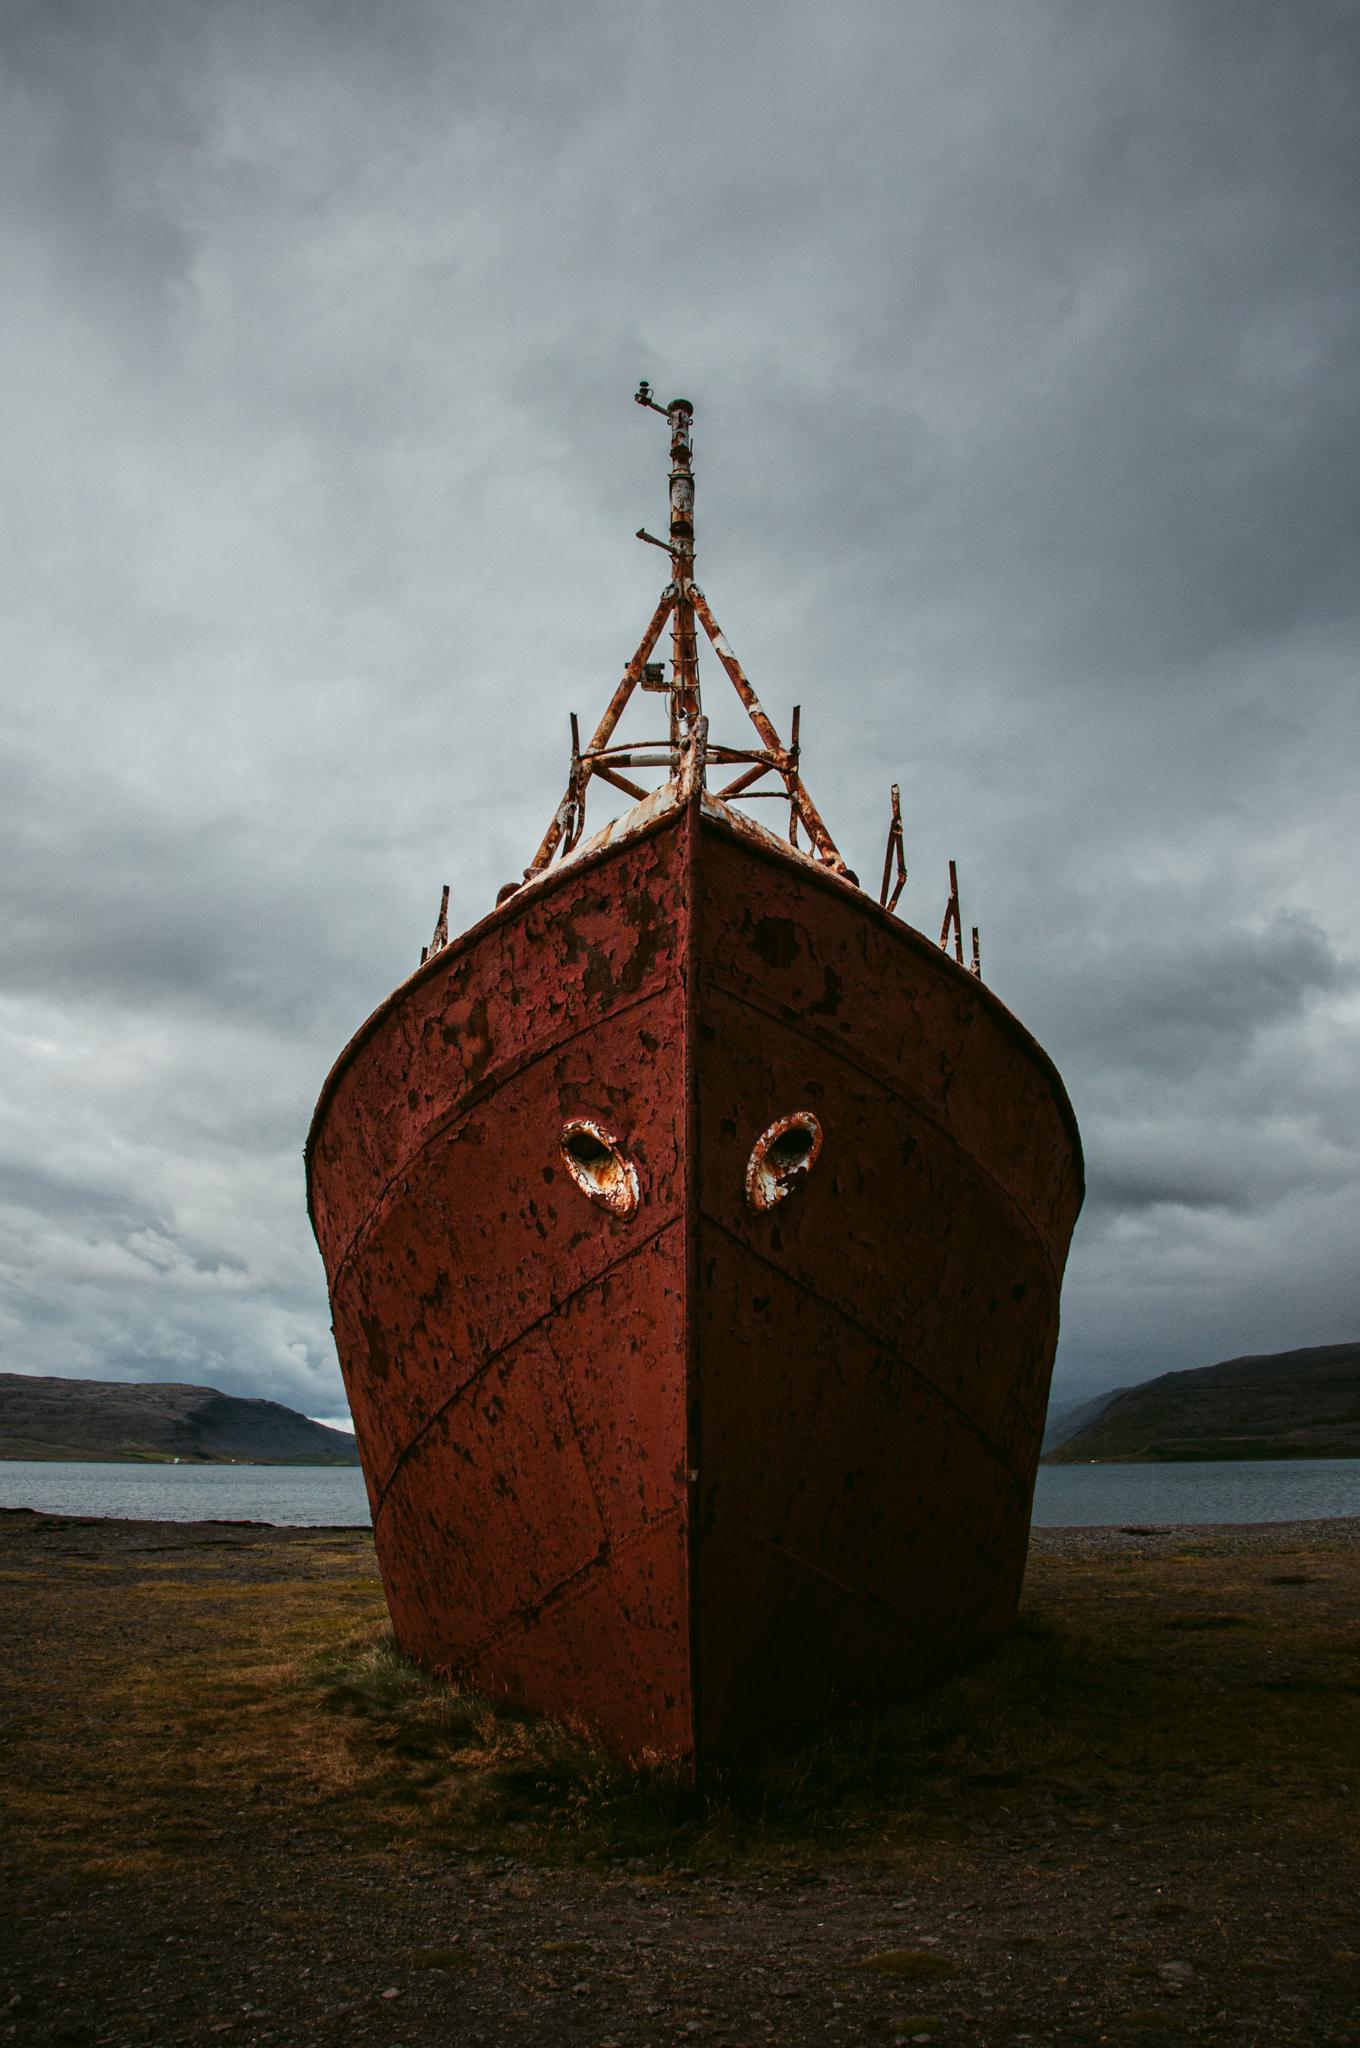
Schiff!
@FotoVorschlag
#ship #iceland #rust #fotoVorschlag #landscapephotography
Alt...
A vertical, eye-level photograph by European Elopement Photographer Sturmsucht captures the rusted hull of an old ship beached on a dark gravel shore under a heavy, overcast grey sky.
The ship’s bow dominates the center of the frame, facing forward. Its weathered metal plates are heavily flaked and covered in a deep rust-red and brown patina. Two circular hawseholes or drainage ports are positioned on either side of the bow's upper ridge, resembling deep-set eyes or nostrils. Rising directly above the bow is a skeletal, triangular metal framework and a vertical mast, stripped of rigging and showing extensive corrosion.
The vessel rests on a narrow, dark, pebbly shoreline interspersed with patches of low, dry grass. In the background, calm dark water stretches horizontally across the middle of the frame, flanked in the distance by low, rolling, barren mountain slopes under the moody, cloud-filled sky. The lighting is diffused and even, emphasizing the textures of rust and stone.

"You fixed something — your change made a program compile when it shouldn't have — and that's proof your API has a major breaking change"
@lorilorusso interviewed me to understand how cargo-semver-checks will catch breakage in your traits and types
https://www.youtube.com/watch?v=38h2OiVI1ms
Enabling the next iteration of the borrow checker on nightly https://lobste.rs/s/fgf5vr #rust
https://blog.rust-lang.org/2026/08/04/enabling-polonius-alpha-on-nightly/
----------------
🛠️ Tool: Atuin - Shell History Synchronization and Search
===================
Atuin is an open-source tool designed to manage, sync, search, and back up shell history with end-to-end encryption.
Key Features:
• End-to-end encryption for shell history
• Client-side encryption before sync
• Built in Rust for performance
• Supports bash, zsh, and fish shells
• Atuin AI assistant for terminal queries
• Self-hosting capabilities for sync servers
Technical Implementation:
Atuin is written in Rust to ensure it does not slow down the shell environment while providing faster history search capabilities. Data is encrypted client-side before synchronization, ensuring commands remain private and accessible only by the user.
Use Cases:
• Maintaining consistent shell history across multiple machines
• Securely backing up command-line workflows
• Querying an AI assistant without leaving the terminal prompt
• Organizations needing self-hosted infrastructure for command history
Installation:
curl --proto '=https' --tlsv1.2 -LsSf https://setup.atuin.sh | sh
Limitations:
Atuin AI is currently free while in testing. The source does not specify performance impacts of the AI feature itself, though the core tool is designed to be unobtrusive.
🔹 atuin #shell #rust #tool #opensource
🔗 Source: https://atuin.sh/
Hot off the presses... Say hello to the first public release of Audio Tetris, the audio-first version of Tetris on Windows written in Rust/WxDragon with the help of Google's Antigravity. I still consider it a beta, but I really want others to kick the proverbial tires. You can get it here: https://github.com/thegregariousdragon/audio-tetris/releases/tag/v1.0.0 Report any issues and feedback is highly encouraged. #A11Y #Accessibility #Blind #AudioGames #Tetris #Rust #WxDragon

Steel-hull boat upkeep.
1. On a calm, sunny day, find a place where you can reach the rust spots from the shore or dock.
2. Sand off the rust and then paint on the rust-blocking primer.
3. Let it dry, and hope not too much dust or plant seeds blow onto the wet paint.
4. Wait for a calm sunny day to paint over primed spots with a top coat, and let it dry.
5. Admire the boat.
6. Go to step 1.
#CanalLife #BoatLife #steel #boat #BoatingLife #boating #narrowboat #hull #rust #maintenance #paint

It's probably about time I got another job.
I'm a Senior Software Engineer, with experience in large scale, high-throughput back-end systems.
I'll put my hand to most things, but I've most recently been doing #Erlang, Kubernetes, etc. at a gambling company.
Strongly prefer remote. London, UK.
Visceral loathing of GenAI and LLMs.
I've recently been messing around with Elixir and Phoenix. I would potentially like to move into #Rust.
My "me" page is at https://rogerlipscombe.me/

It's Friday again, so it's time for another update on the work on Diesel, a ORM and query builder for Rust.
I published Diesel 2.3.12 today, which bumps the maximal supported libsqlite3-sys version to 0.38 and fixes an precision issue with Mysql's TIME types. See the release announcements for more details: https://github.com/diesel-rs/diesel/releases/tag/v2.3.12
We received no new bug report, but 10 new PR's this week. Several of the new PR's seek to add large new features so this required quite a bit of review time. Any help with reviewing changes to Diesel is welcome.
Introducing Kitesurf: The agent-first browser that runs in V8 isolates on Cloudflare Workers https://lobste.rs/s/9bxkgi #browsers #rust #vibecoding
https://blog.cloudflare.com/kitesurf/
Just One Function, 10x Faster? Reading a Rust Performance PR https://lobste.rs/s/sv9hwi #performance #rust
https://greptime.com/blogs/2026-07-31-prom-read-conversion-optimization

Time for the most popular of the bunch, as reliably measured in #GitHub stars ★
I haven't touched this one in a while, though there's a decent chance I’ll pick it back up using #Frida's #Rust bindings (see the previous post in this mini-series 🦀)
A collection of my Frida instrumentation scripts for reverse engineering mobile apps (and a few non-mobile targets that snuck in along the way):
https://github.com/0xdea/frida-scripts

FLOSS Weekly Episode 878: A Tool With Opinions https://hackaday.com/2026/08/05/floss-weekly-episode-878-a-tool-with-opinions/
#HackadayColumns #Podcasts #Embedded #FLOSSWeekly #Rust
Sovereign Tech Fellowship for Rust maintenance (June-July 2026 report) via @bd103 https://lobste.rs/s/0zr9wr #compilers #devops #performance #rust
https://kobzol.github.io/rust/2026/08/03/stf-june-july-2026.html

LabubaRAT has been added to the Rust Malware Sample Gallery: https://github.com/decoderloop/rust-malware-gallery#labubarat
#rust #rustlang #malware #infosec #ReverseEngineering #MalwareAnalysis #reversing #LabubaRAT
IronWorm, a Rust-based infostealer observed in several recent supply chain compromise incidents, has been added to the Rust Malware Sample Gallery: https://github.com/decoderloop/rust-malware-gallery#ironworm
#rust #rustlang #malware #infosec #ReverseEngineering #MalwareAnalysis #reversing #IronWorm #SupplyChain #infostealer
A Rust-based clipboard hijacker used in a "Ghost Network" malware distribution campaign has been added to the Rust Malware Sample Gallery: https://github.com/decoderloop/rust-malware-gallery#rust-based-clipboard-hijacker-used-in-ghost-network-malware-distribution-campaign
#rust #rustlang #malware #infosec #ReverseEngineering #MalwareAnalysis #reversing
JitterDropper has been added to the Rust Malware Sample Gallery: https://github.com/decoderloop/rust-malware-gallery#jitterdropper
Thank you to 0xnubb for the contribution!
#rust #rustlang #malware #infosec #ReverseEngineering #MalwareAnalysis #reversing #JitterDropper
#FPIndia is looking for #meetup hosts in #Bangalore
Connect with senior devs and architects
Showcase your engineering culture
Engage with the community!
We need a space for 20 to 40 people and a screen for ~3 hours
DM or comment!
#FunctionalProgramming #haskell #elixir #rust #clojure #typescript #scala #purescript #formalmethods
rust-lang/rust is adopting an LLM policy via @wezm https://lobste.rs/s/czvkjy #rust
https://blog.rust-lang.org/inside-rust/2026/08/05/rust-langrust-is-adopting-an-llm-policy/


rust-lang/rust is adopting an LLM policy
If you personally use LLMs and want to contribute to the Rust toolchain, you *really* should read it.
The summary is "It's fine to use LLMs to answer questions, analyze, distill, refine, check, suggest, review. But not to *create*." Effectively, no other human should see LLM output, unless they ask for it, and LLM usage shall be disclosed.
https://blog.rust-lang.org/inside-rust/2026/08/05/rust-langrust-is-adopting-an-llm-policy/
designing a query system via @fanf https://lobste.rs/s/awdorz #compilers #rust
https://bal-e.org/speed/krabby/2026/query-system-design/
Don't stop early: Case-folding source code at memory speed via @fanf https://lobste.rs/s/qsgcgz #performance #rust
https://github.blog/engineering/architecture-optimization/dont-stop-early-case-folding-source-code-at-memory-speed/